INFRA
SECURITY
Agentless Cloud Misconfiguration Scanning (CSPM) with CIS and NCA ECC/SAMA Policy Packs
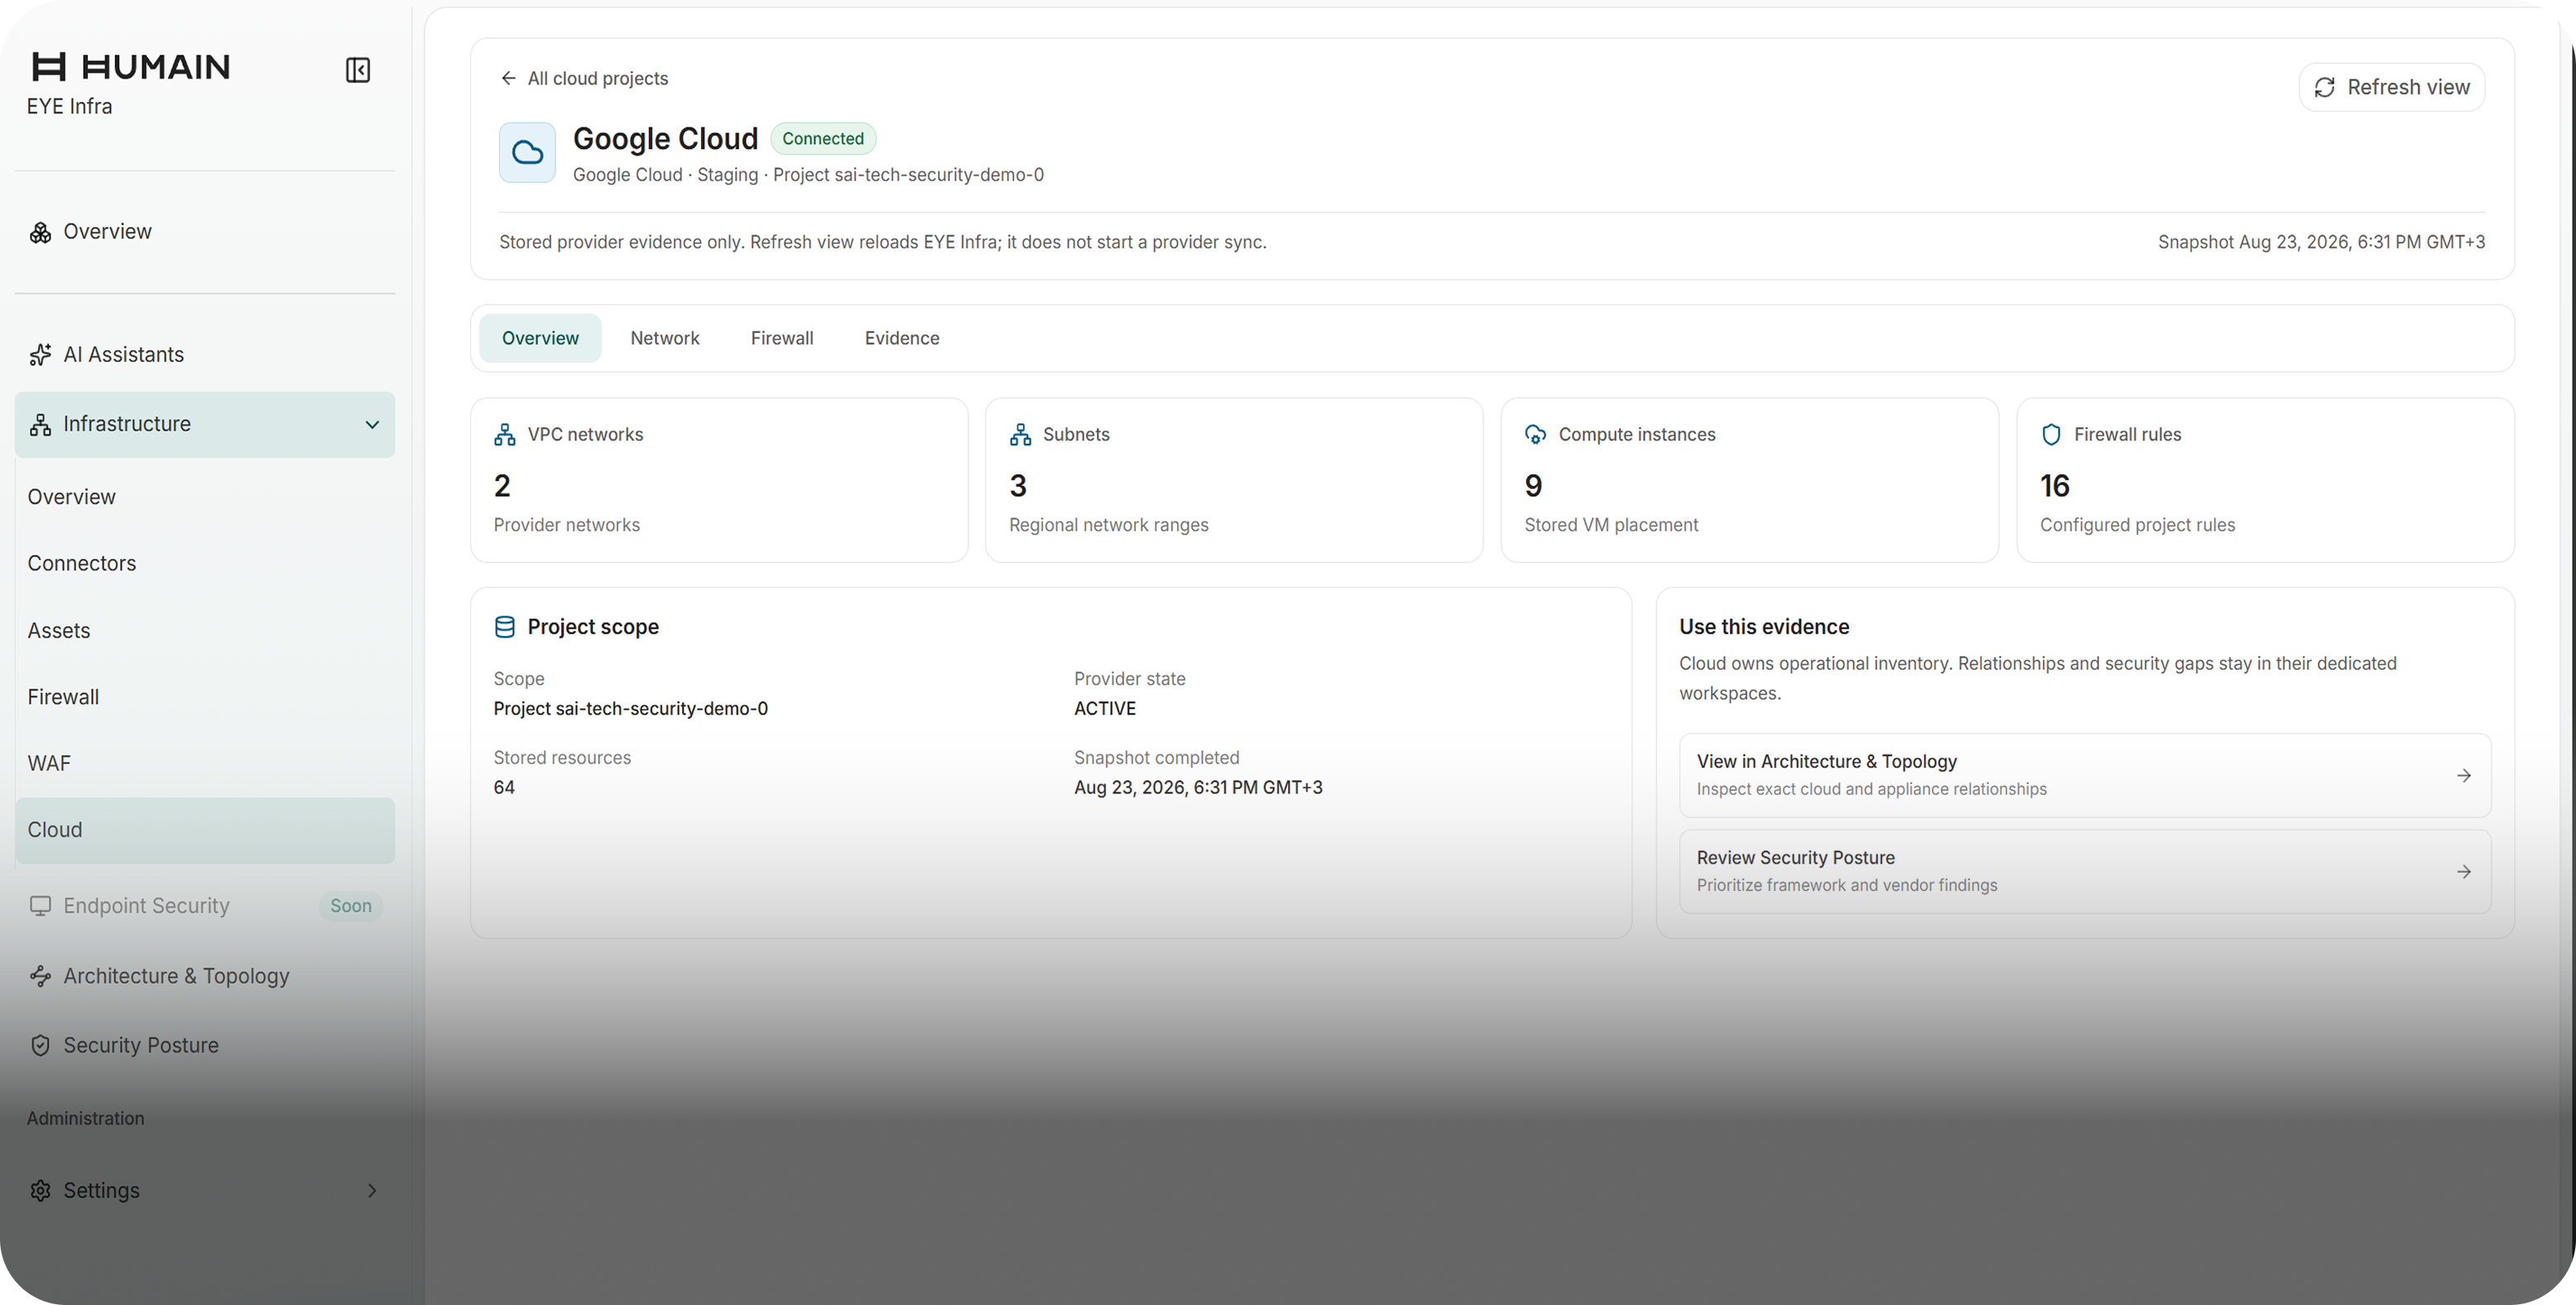
CLOUD
SECURITY
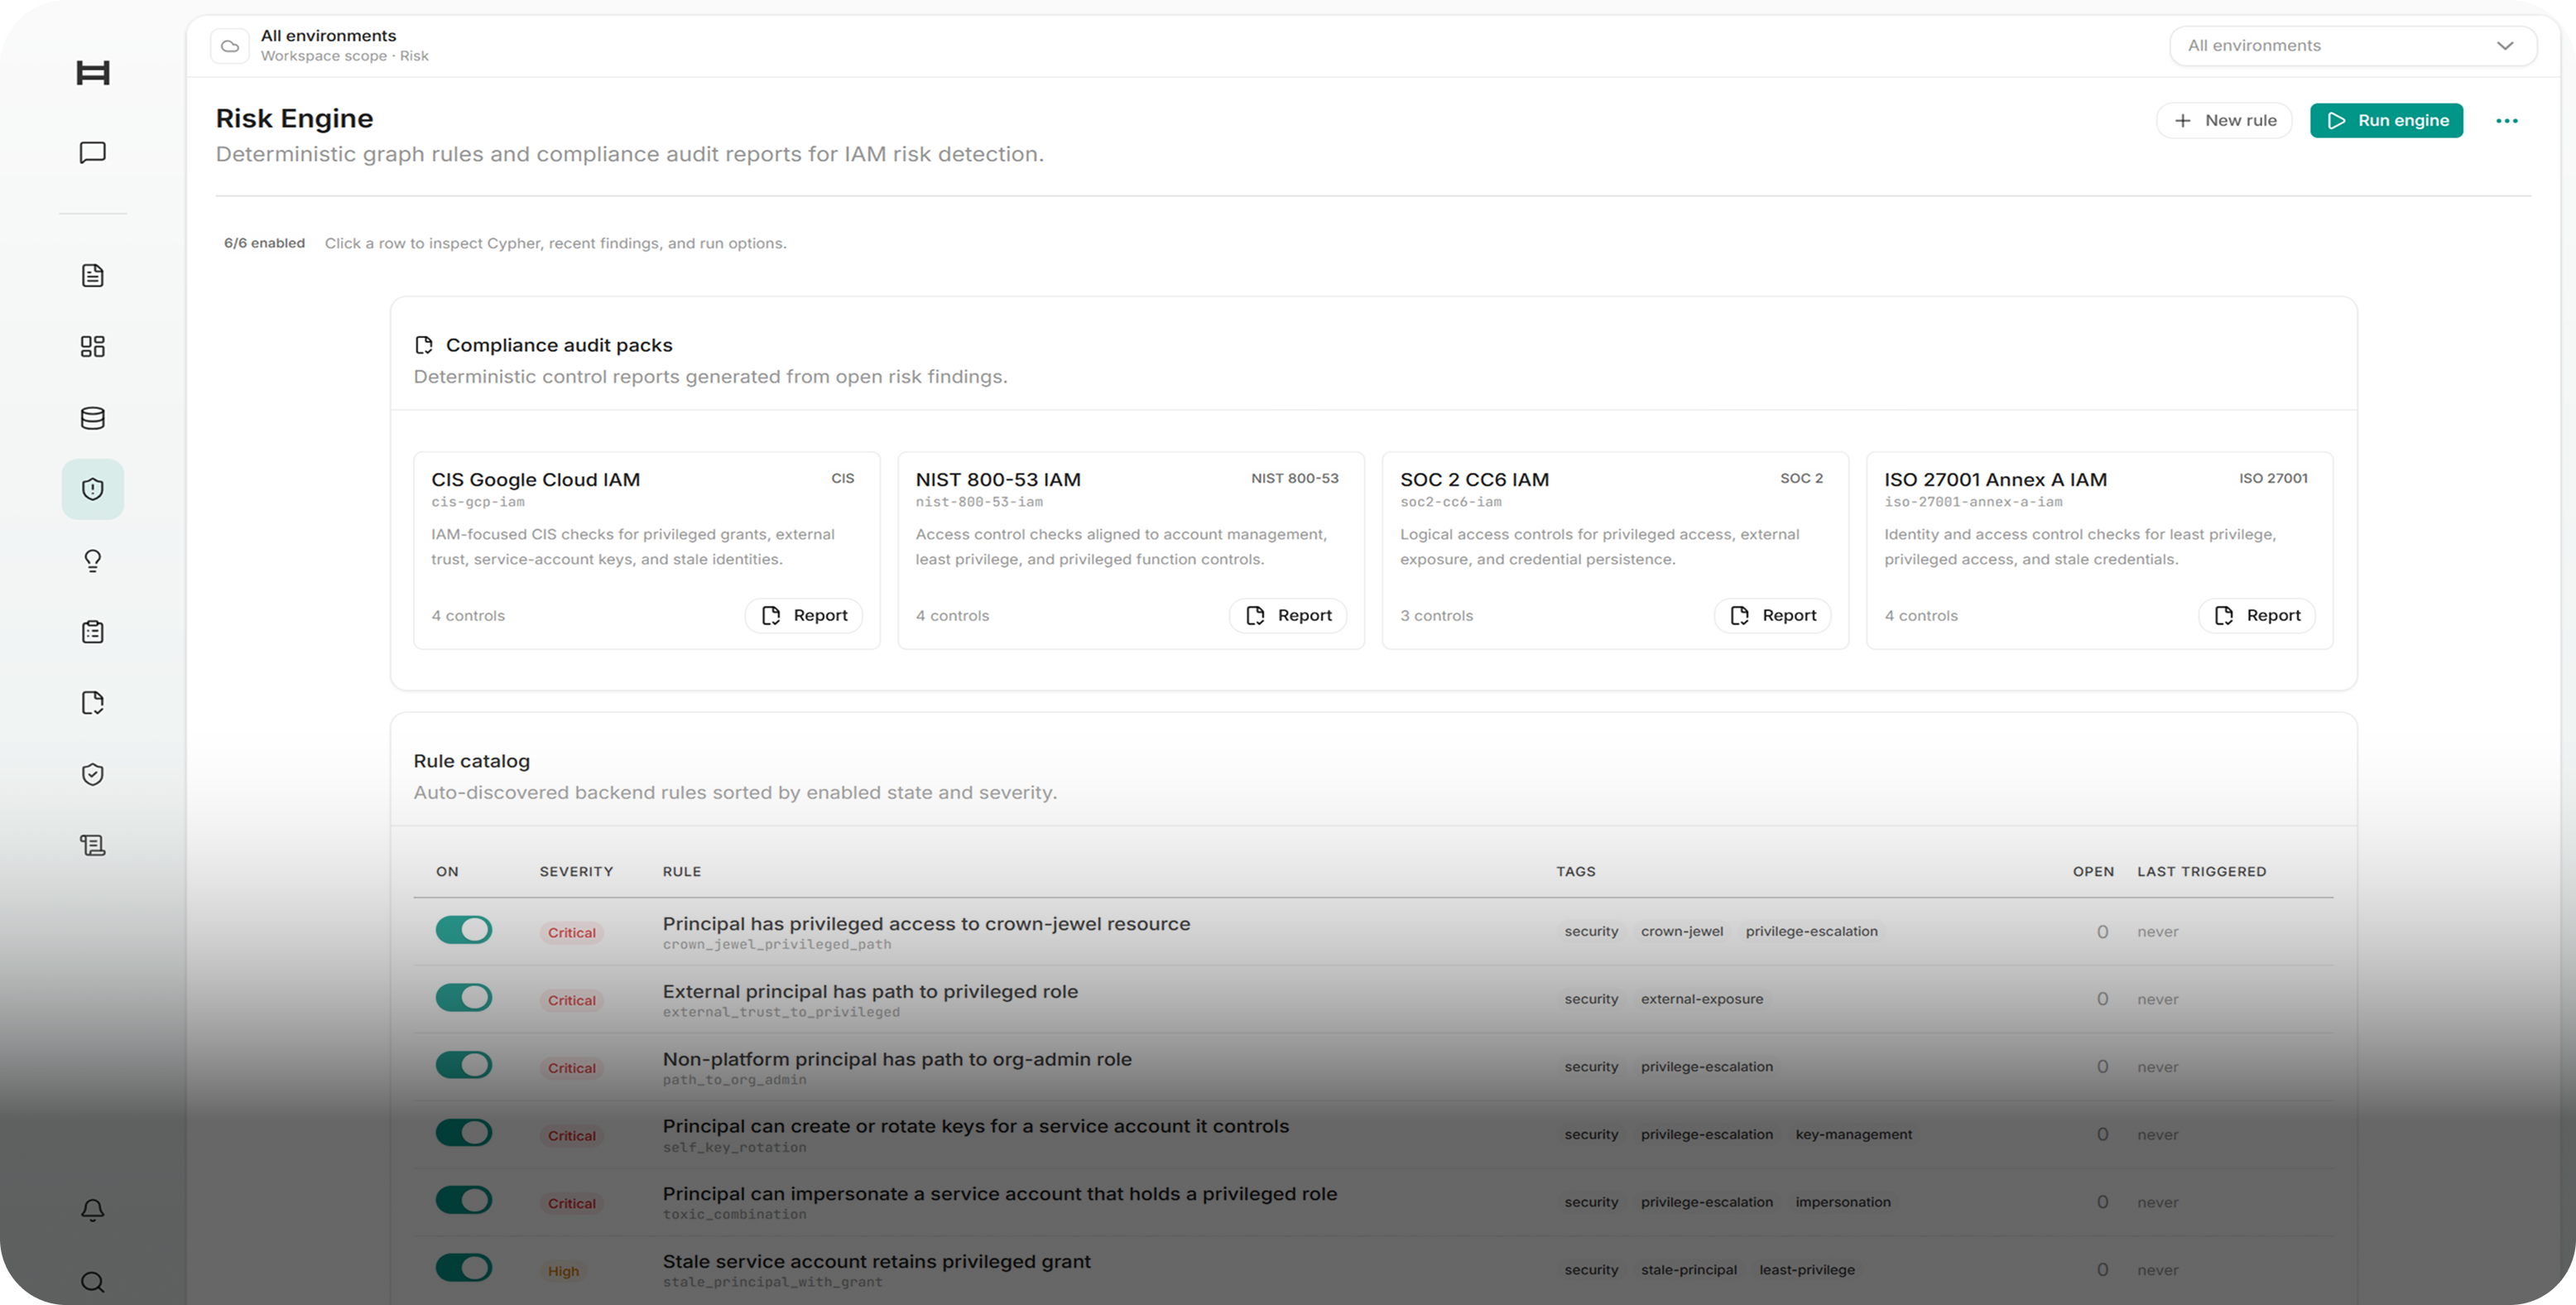
Continuous Compliance Monitoring for Cloud Environments with Custom Policy Templates
INFRA
SECURITY
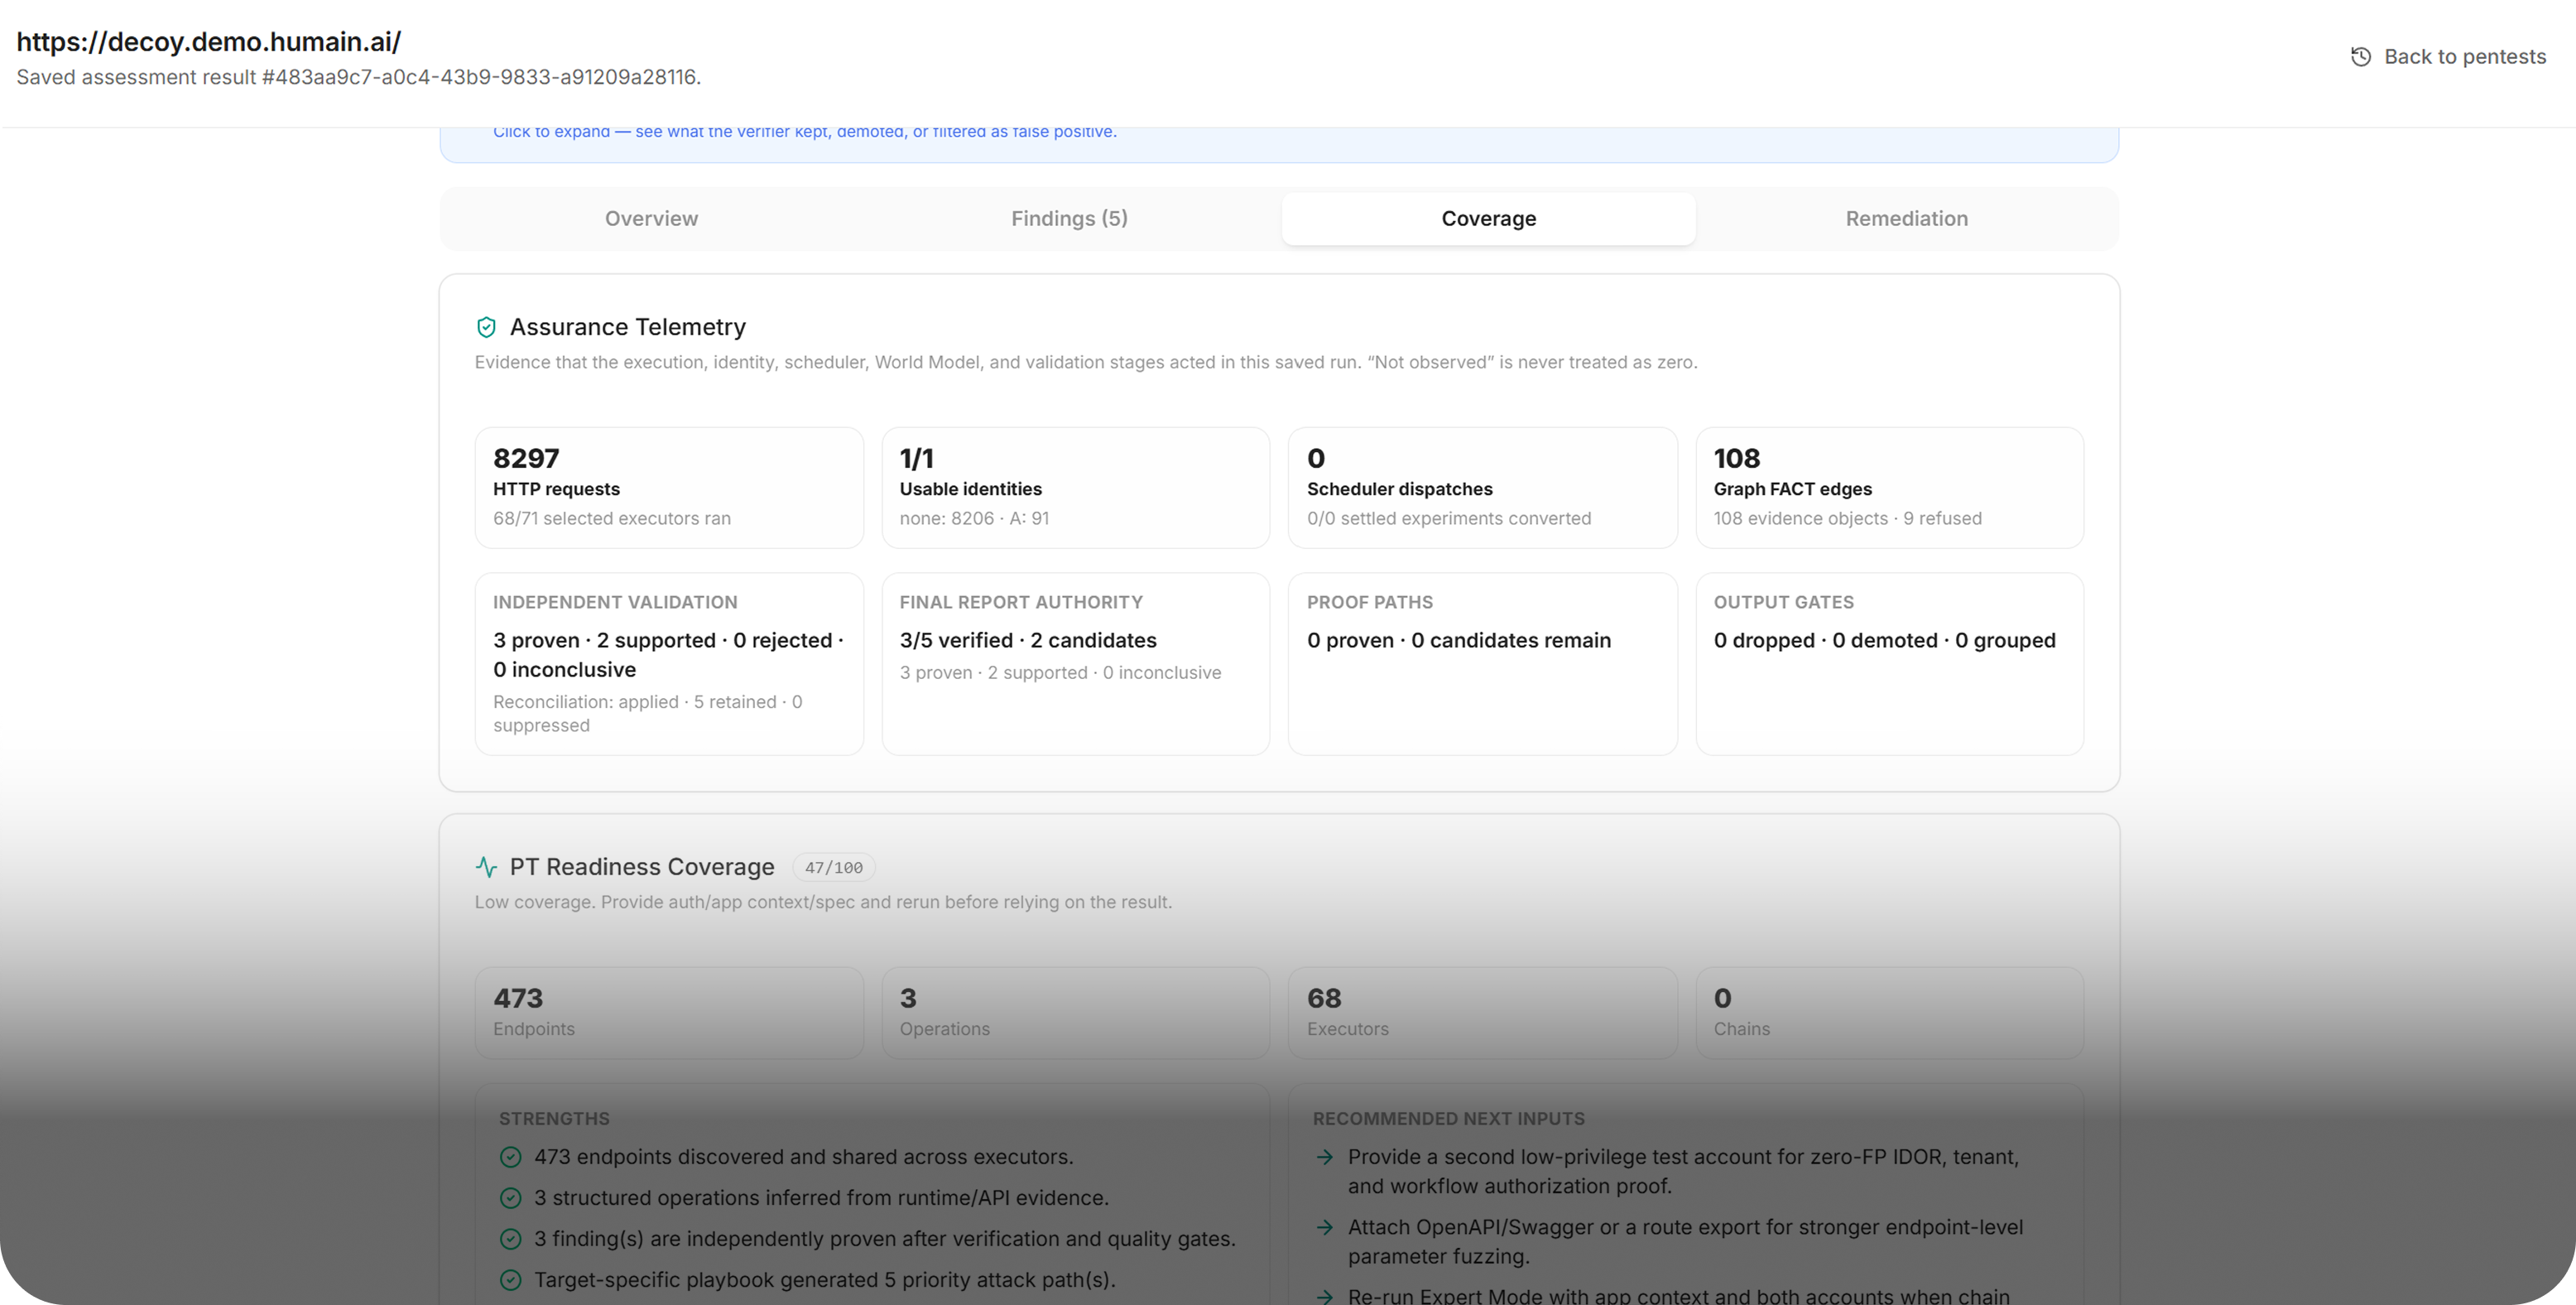
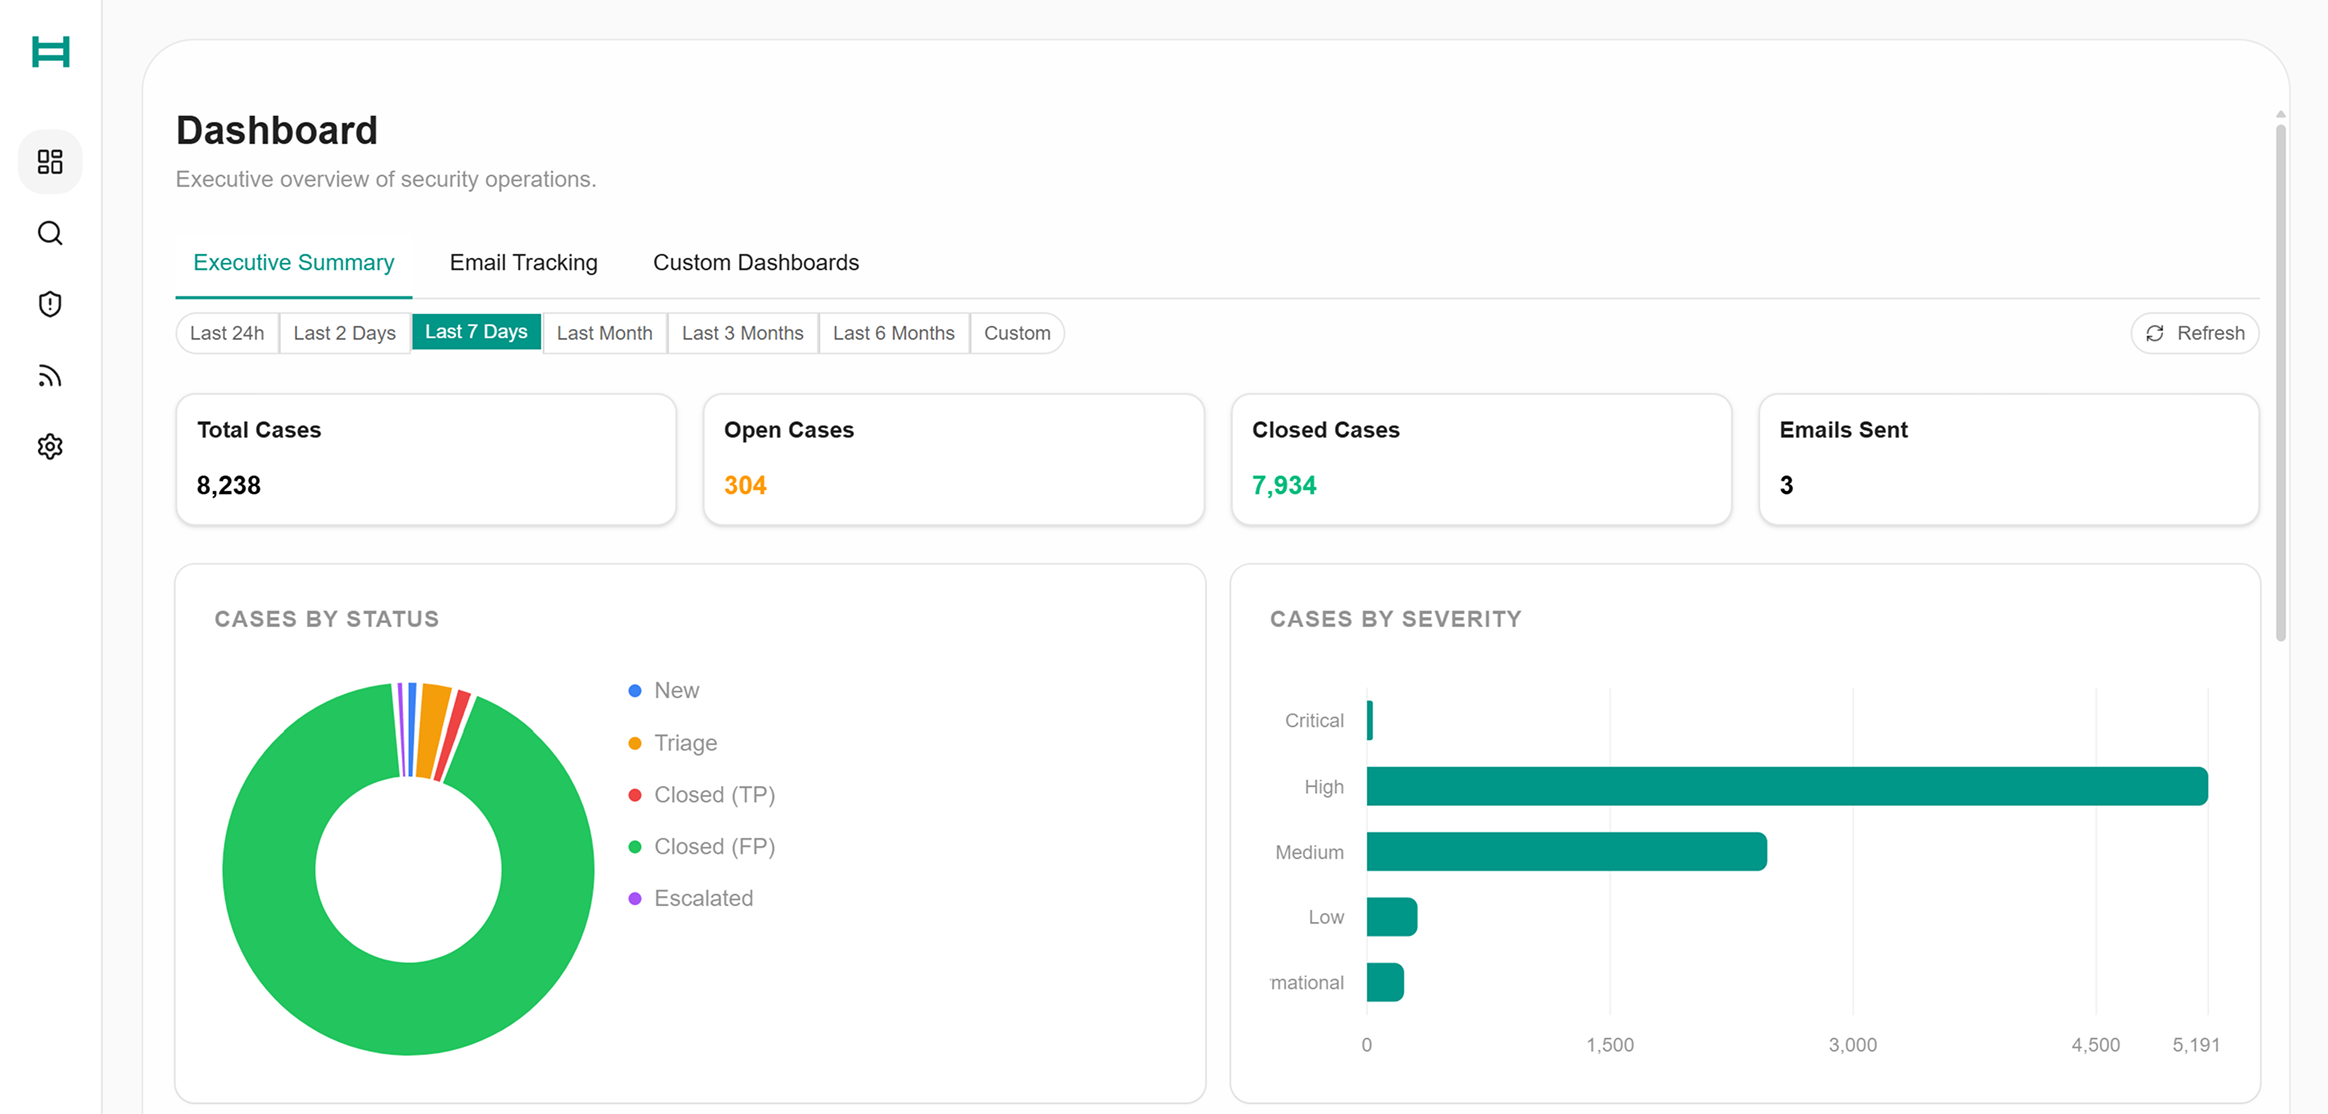
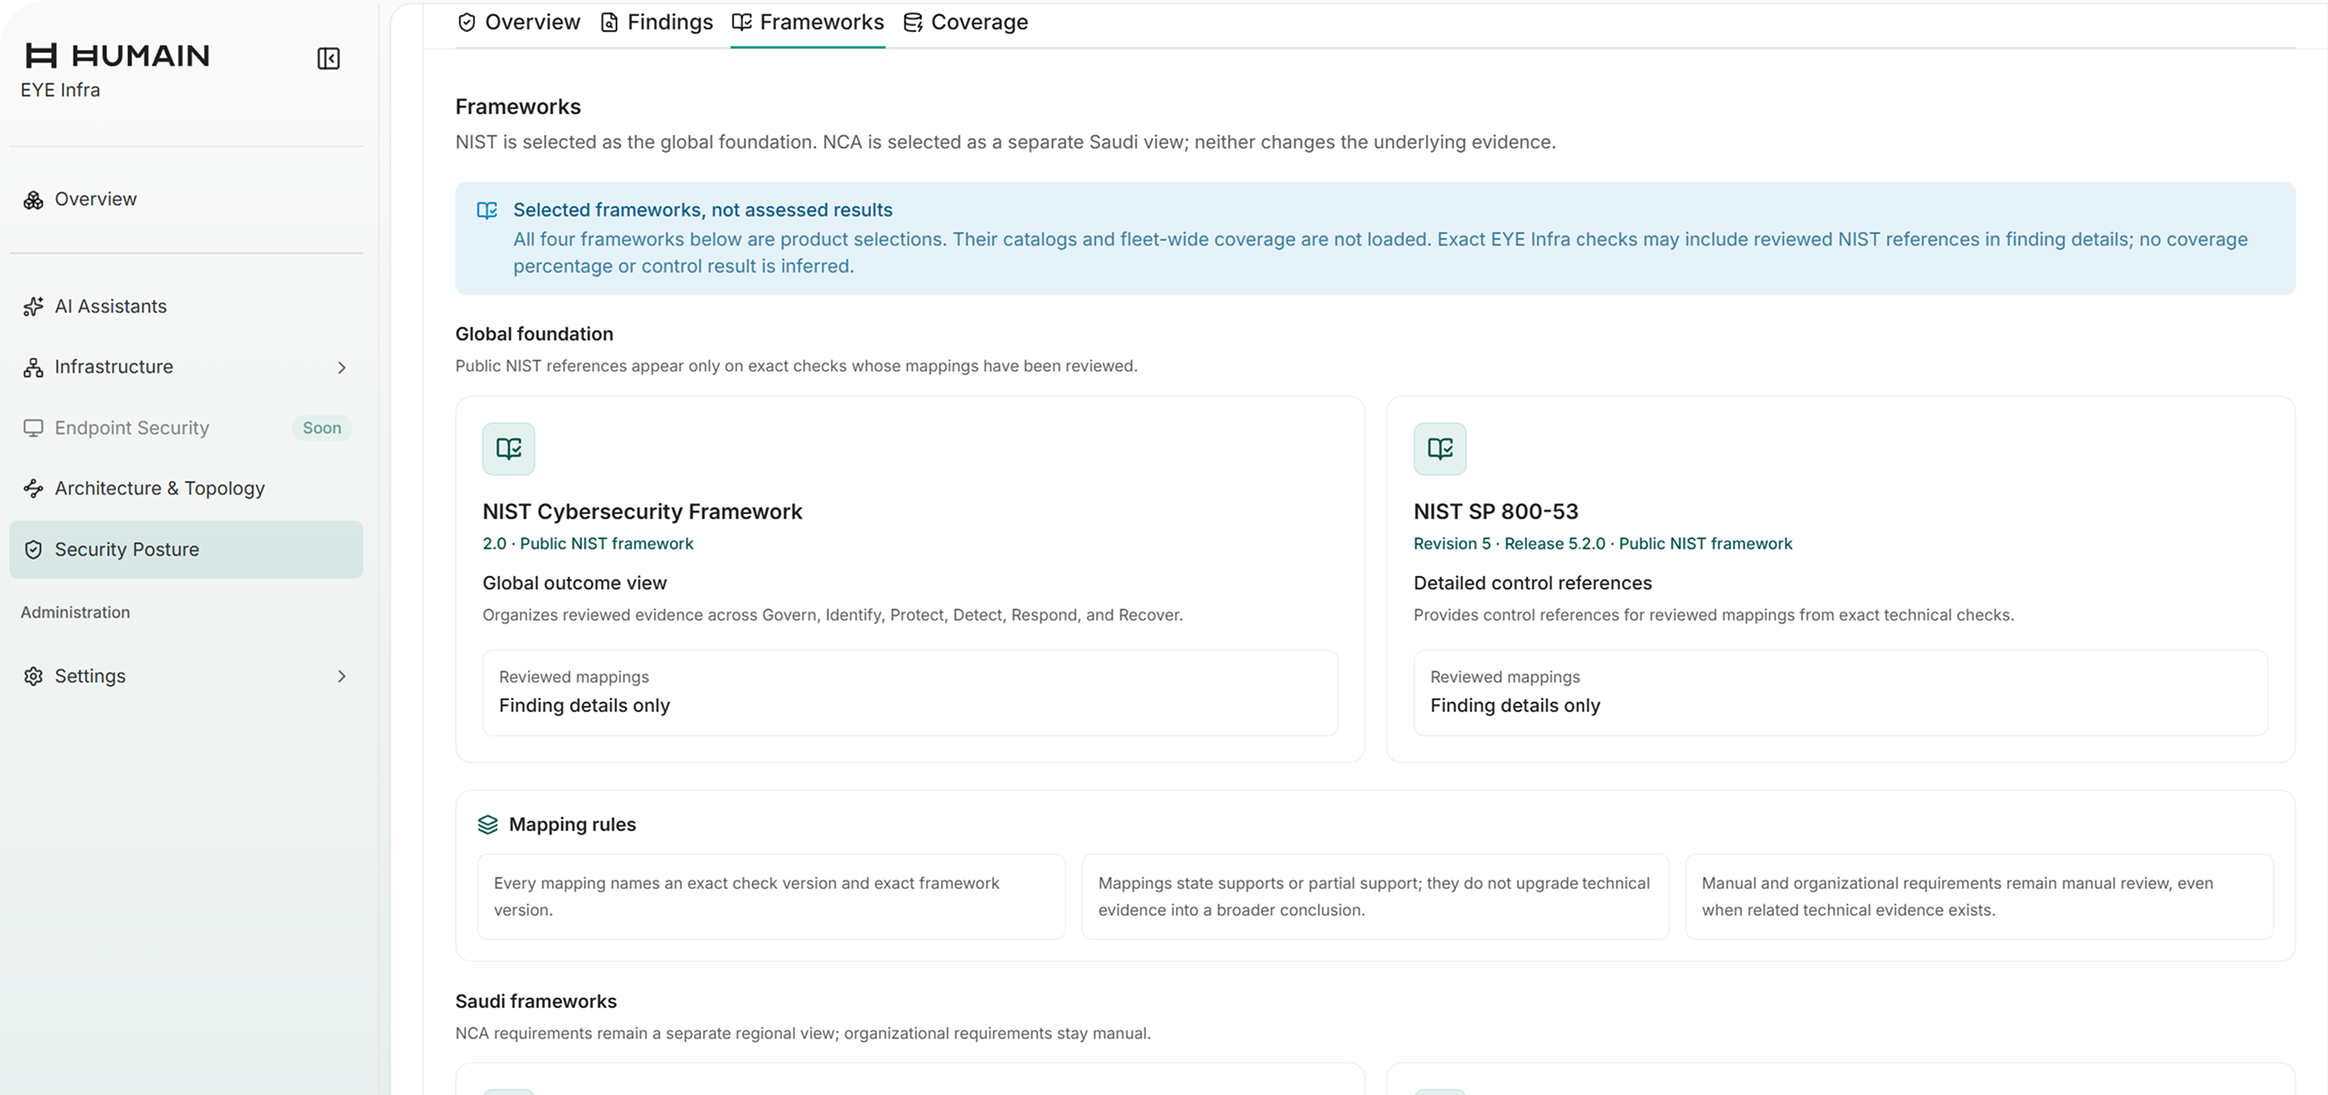
Unified Posture & Coverage Dashboard
APPLICATION SECURITY
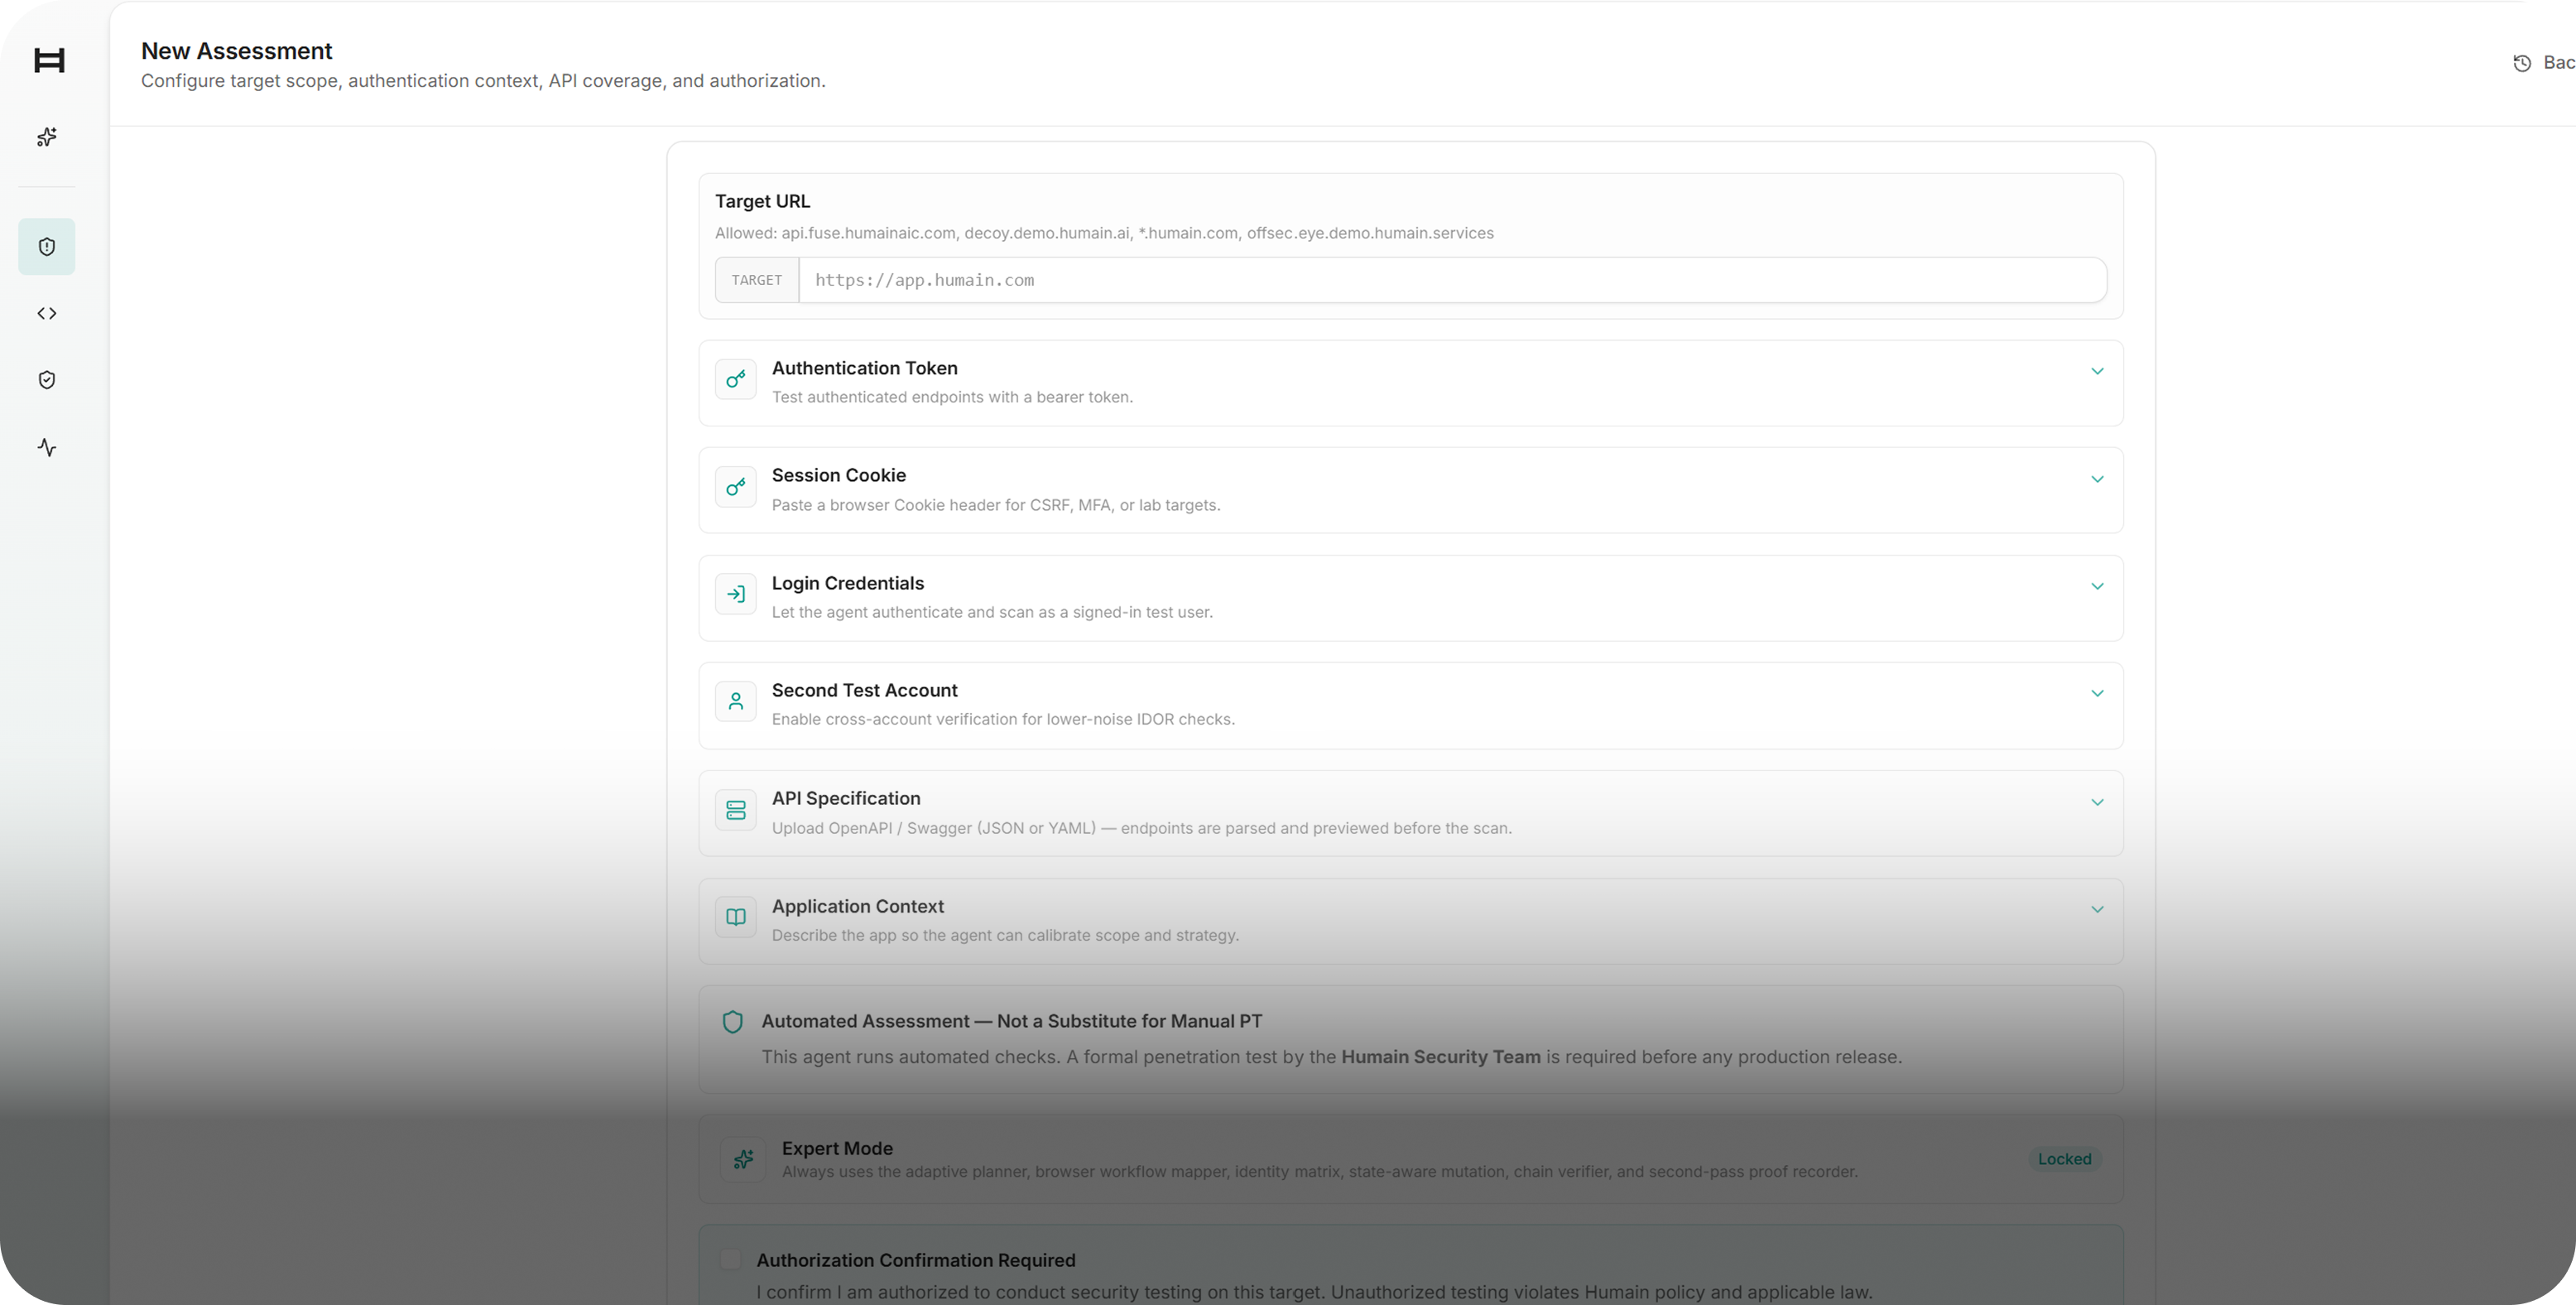
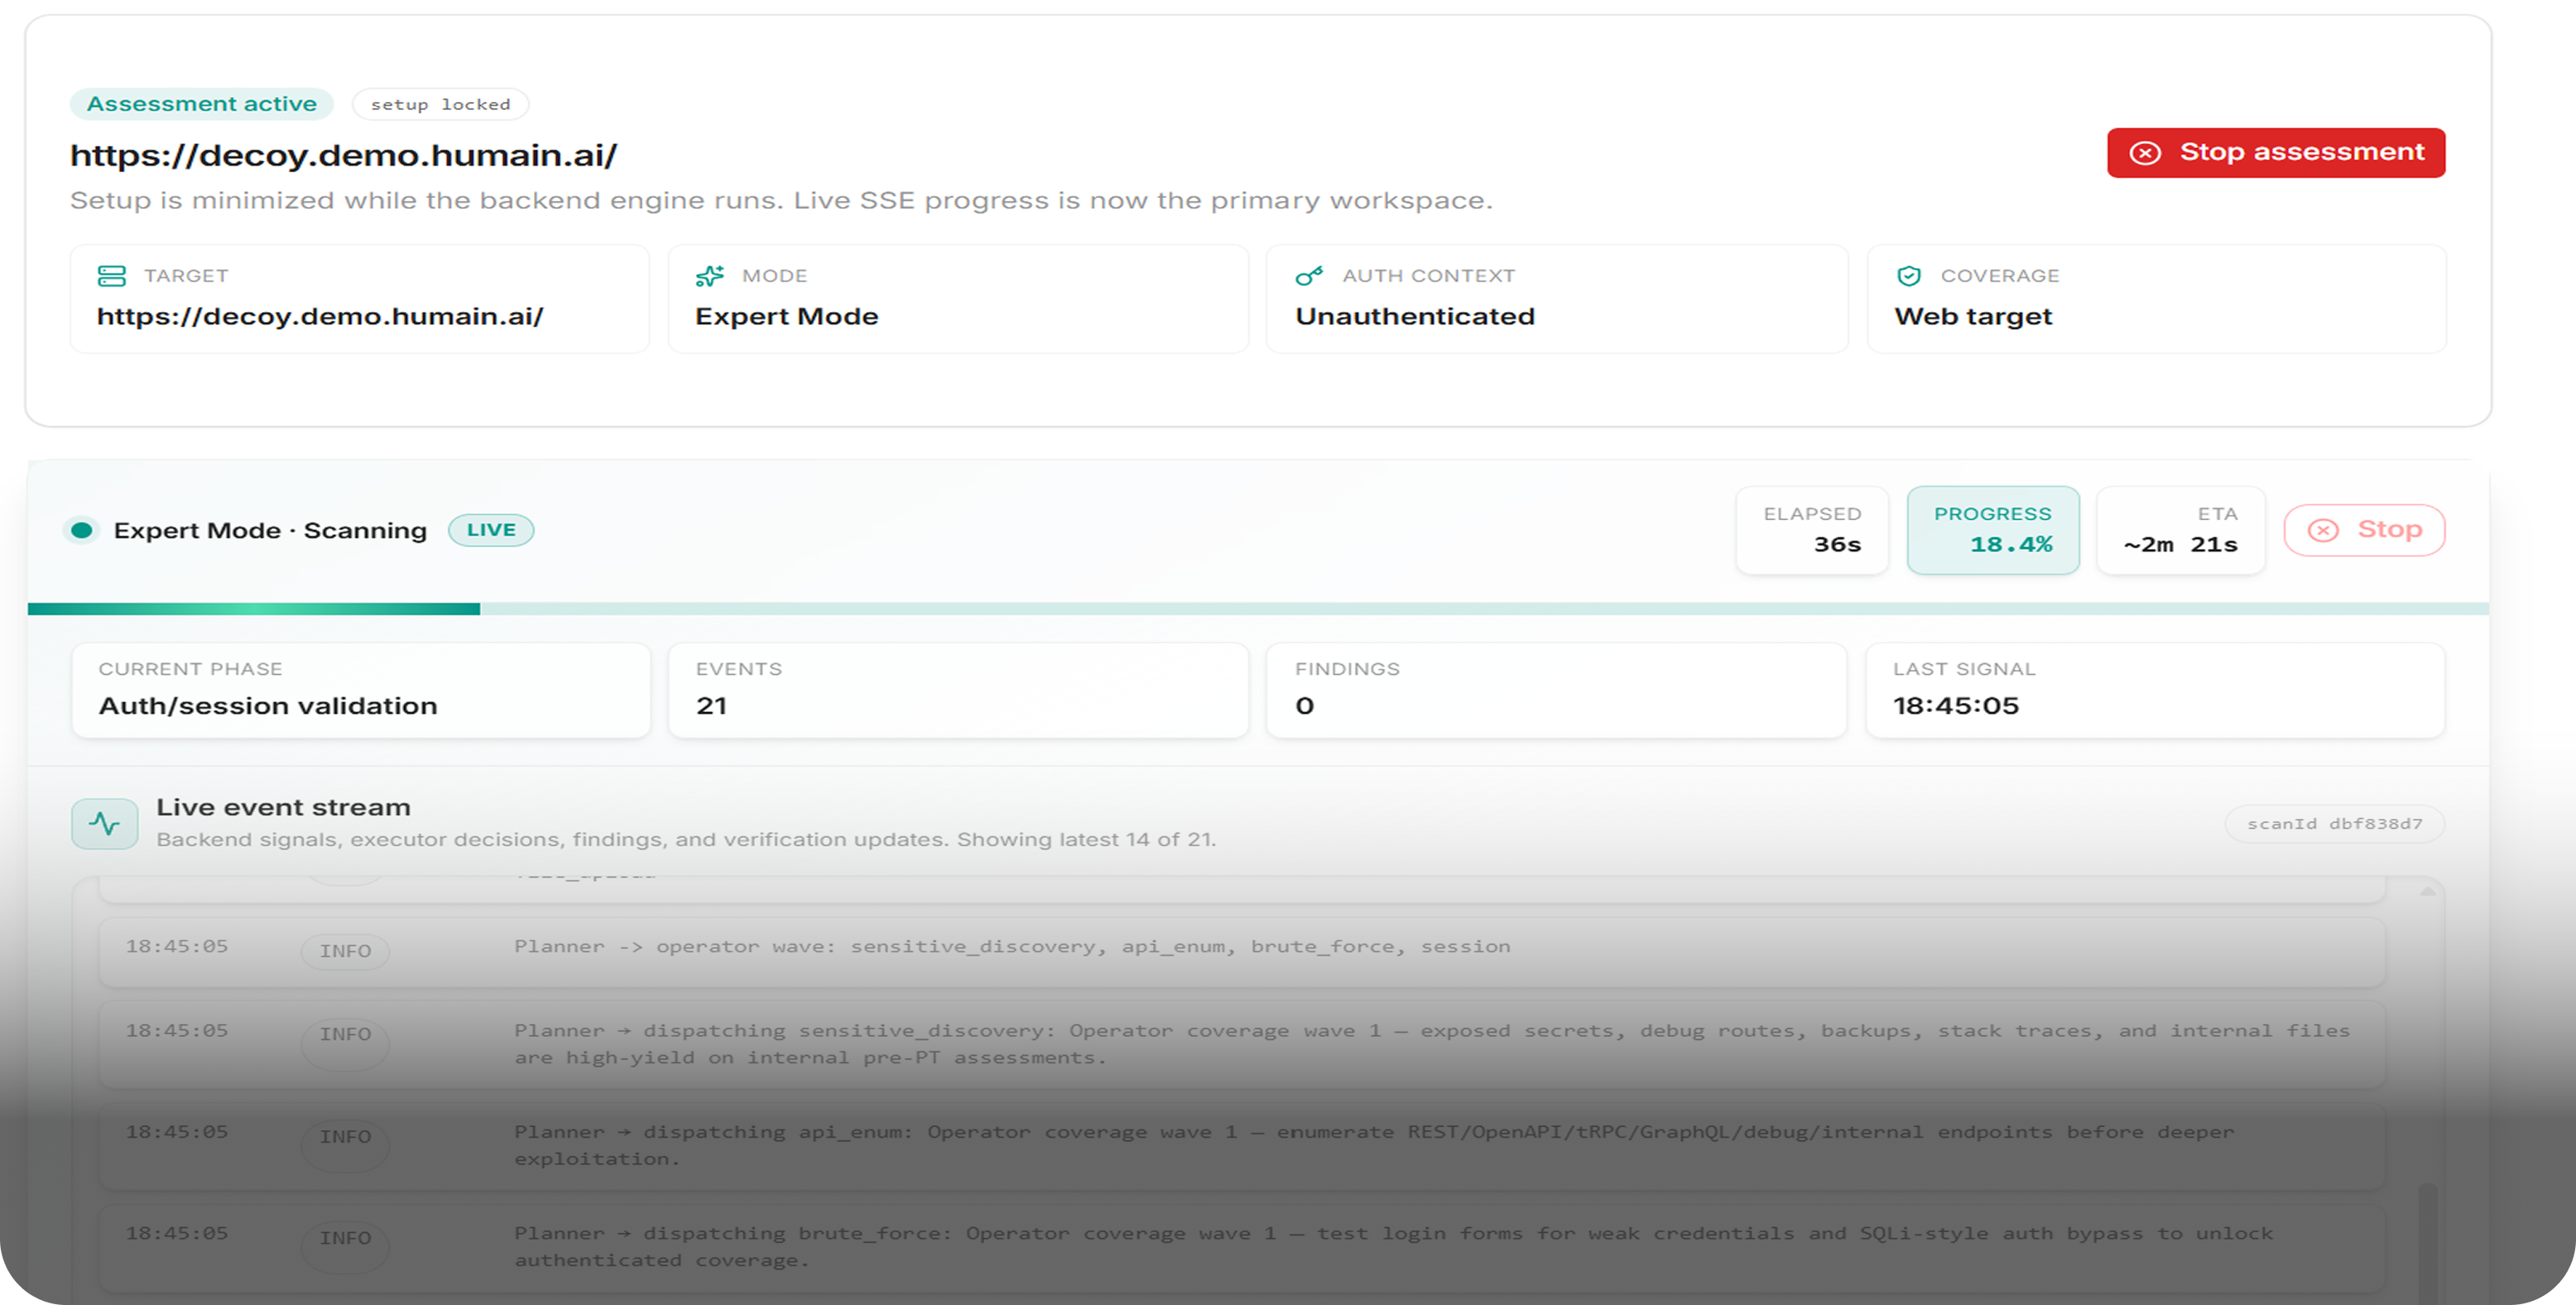
Rules-of-Engagement Control Plane, In-Path Scope Enforcement and Ten-Second Kill Switch
APPLICATION SECURITY
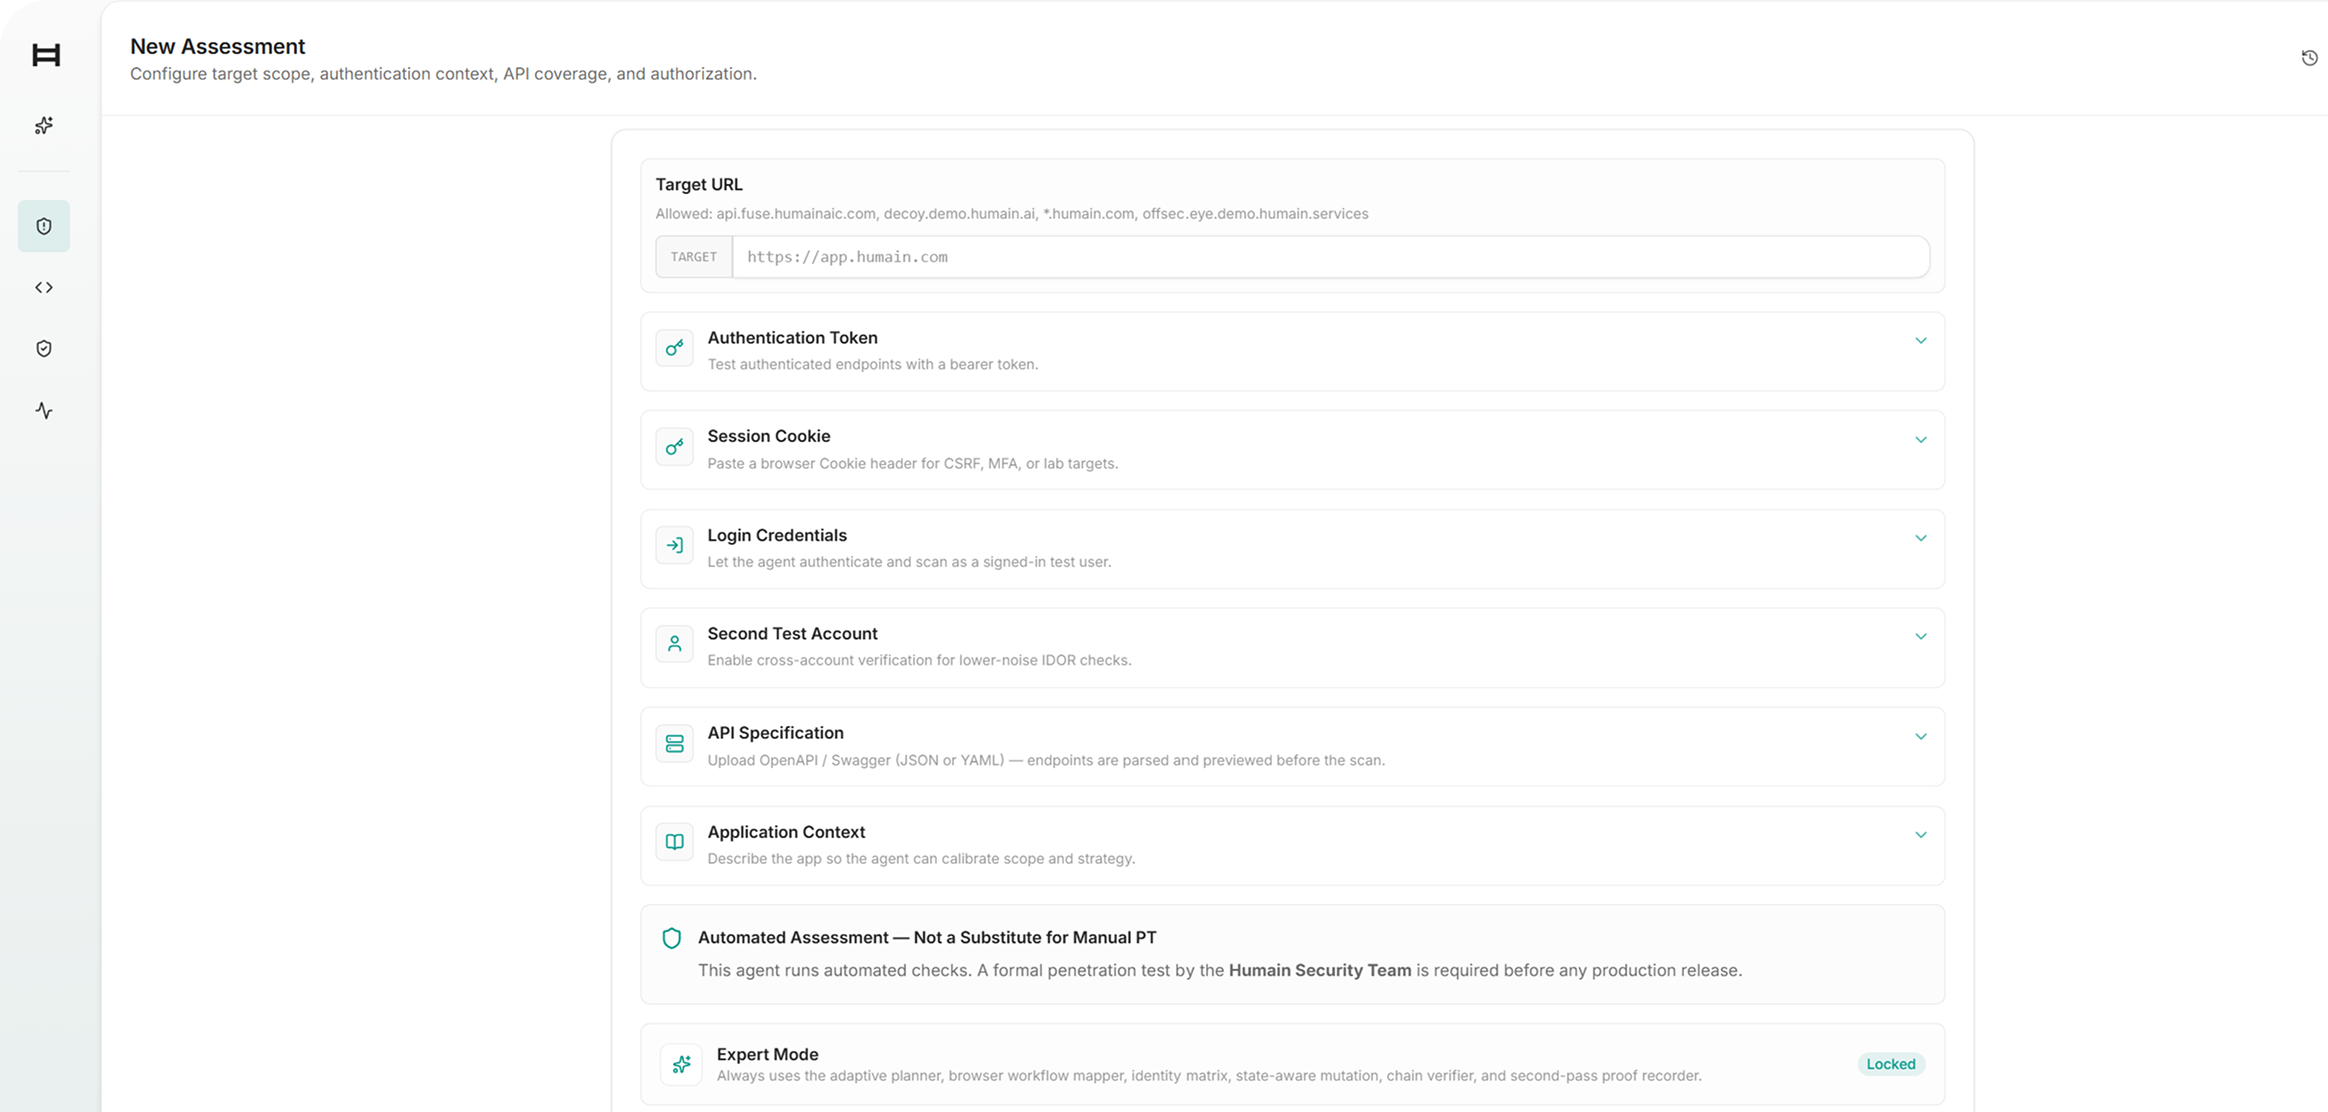
Authorized Campaign and Target Configuration
SOC
& SIEM
Deterministic Rules Engine for Sub-Second Auto-Close
SOC
& SIEM
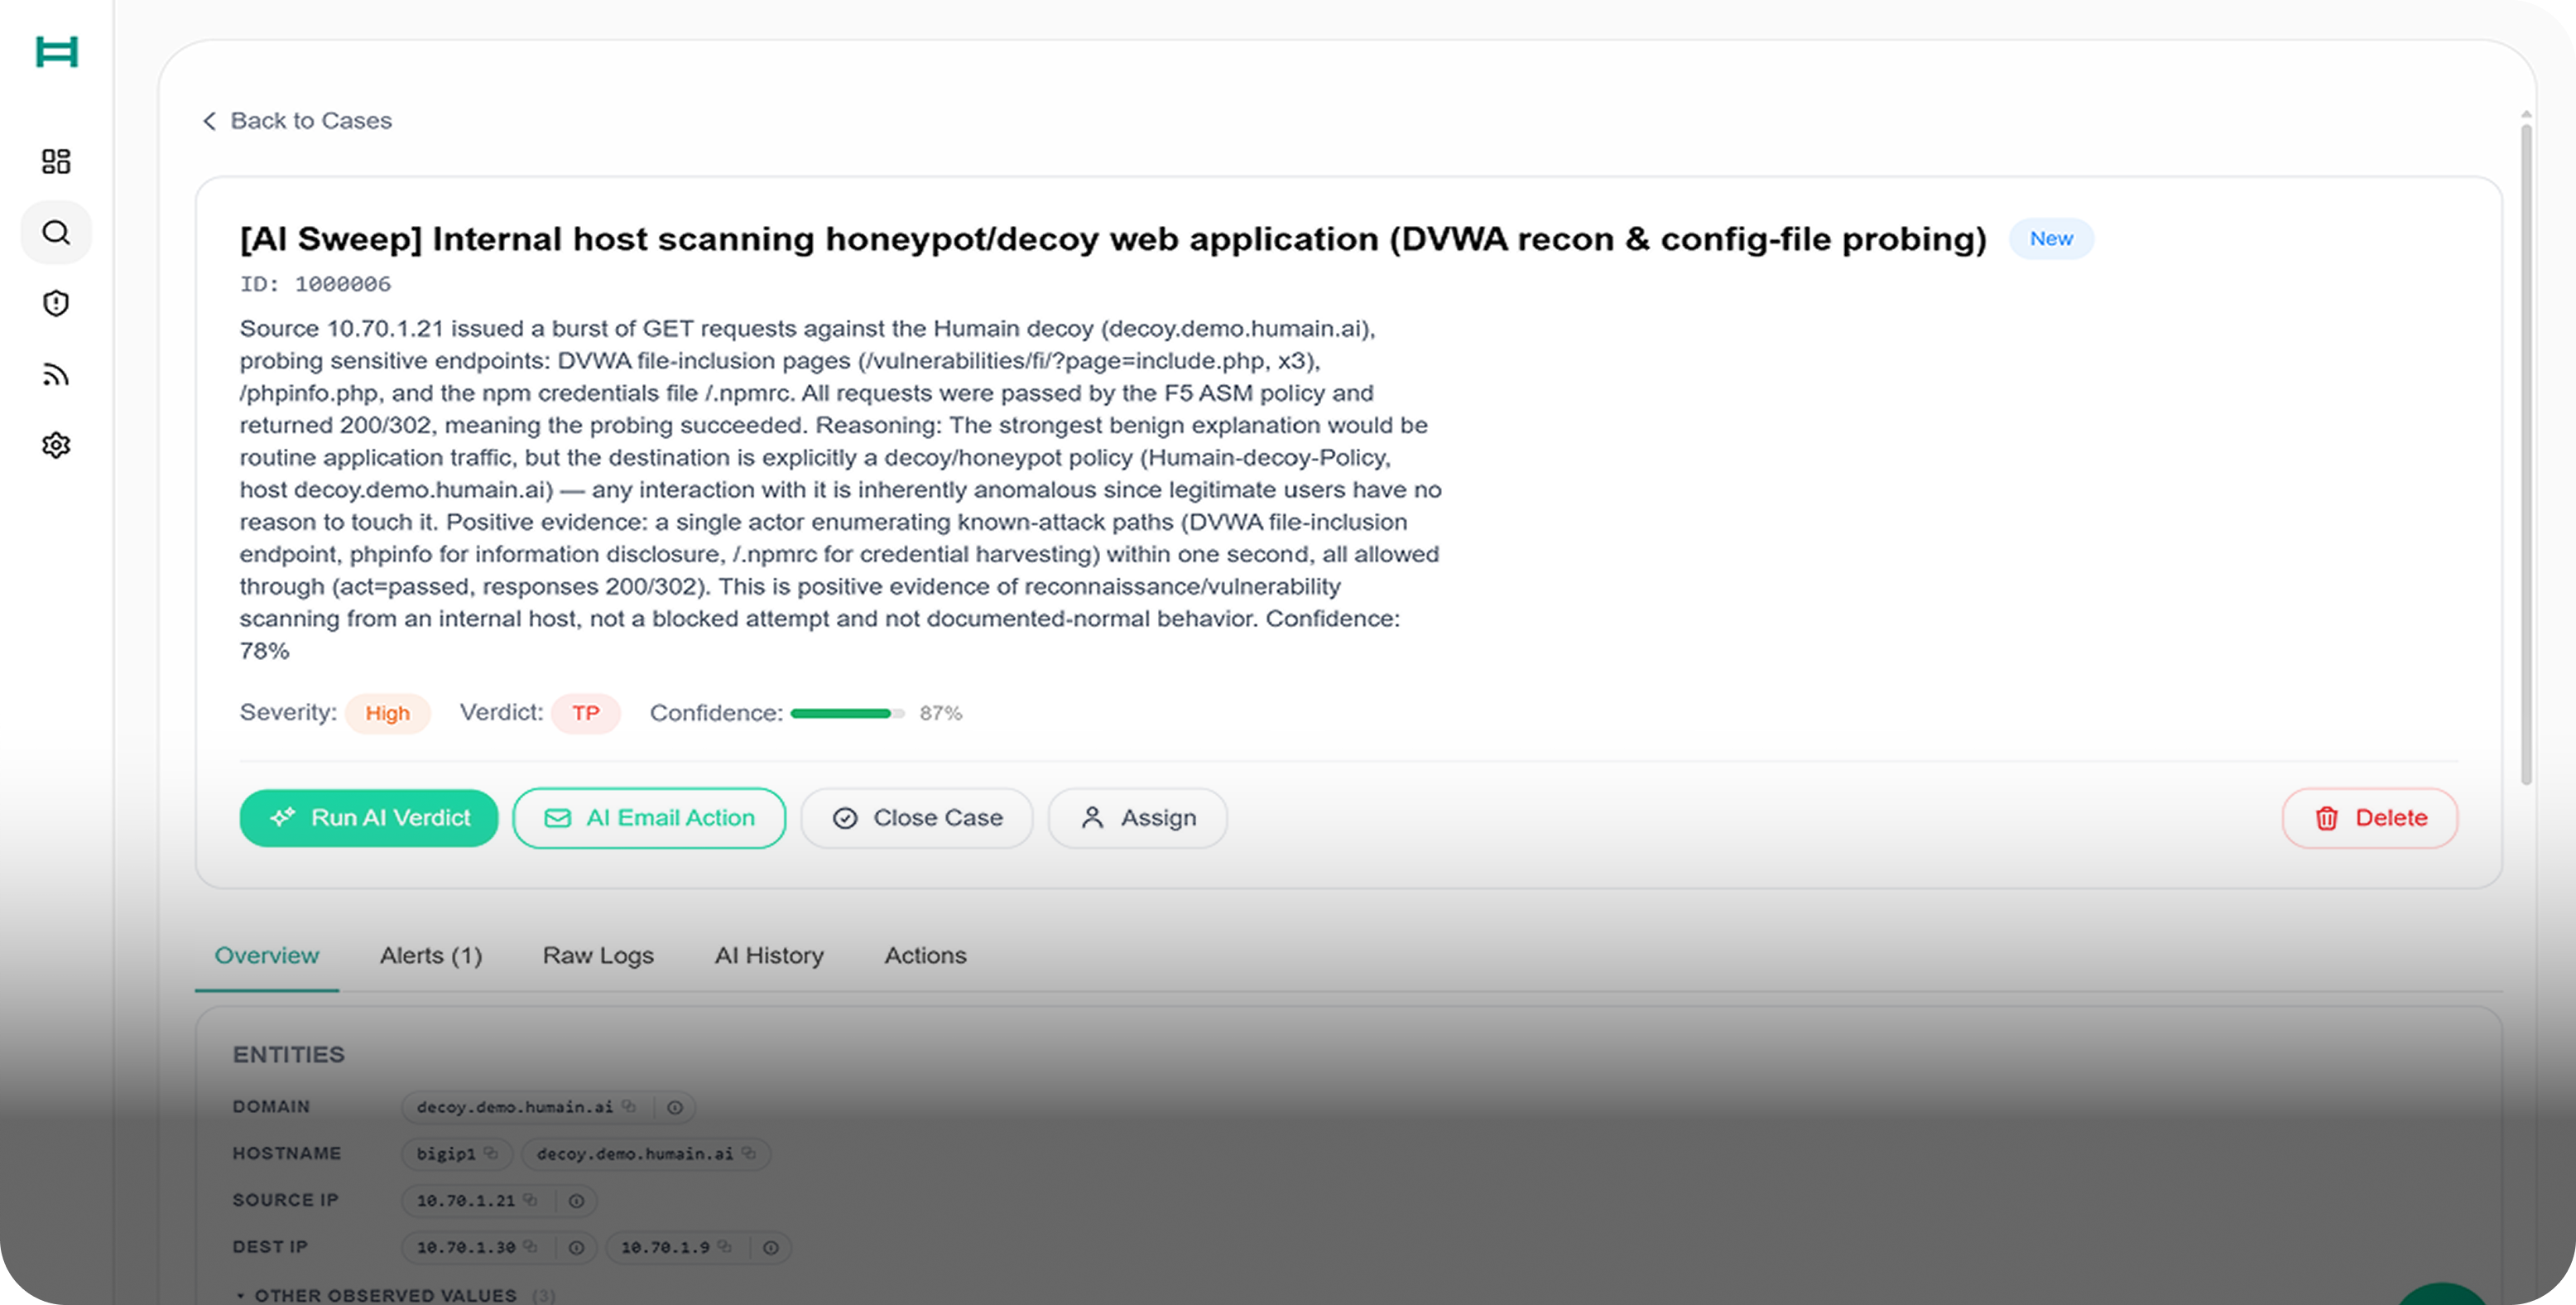
Confidence-Thresholded LLM Auto-Close with Human Override
SOC
& SIEM
LLM Verdict Pipeline for Tier-1 Alert Triage
SOC
& SIEM
Case Timeline, Evidence Pack and Executive Summary
SOC
& SIEM
Raw Log Ingestion Platform (Any source)
IAM
HUB
One-Click PDF Audit Evidence Reports Mapped to NCA ECC, SAMA CSF and ISO 27001
IAM
HUB
Environment Baseline and Approved-Exception Memory
INFRA
SECURITY
Asset Lifecycle Governance: Classification, Ownership and Approval Gates
INFRA
SECURITY
Cloud & Kubernetes Read-Only Onboarding Connectors with Least-Privilege Templates
APPLICATION SECURITY
Cross-Scanner Deduplication & Canonical Vulnerability Identity Resolution
APPLICATION SECURITY
Latest-Commit Changed-Code Review
APPLICATION SECURITY
Secure Self-Hosted GitLab Repository Onboarding
INFRA
SECURITY
Unified Asset & Application Inventory with Cross-Source Deduplication
INFRA
SECURITY
Symantec Endpoint Integration with Endpoint & Patch Hygiene Scoring
APPLICATION SECURITY
Multi-Scanner Findings Ingestion & Normalisation Pipeline (Qualys, Tenable, Sysdig, Nessus,
CSV/SARIF)
IAM
HUB
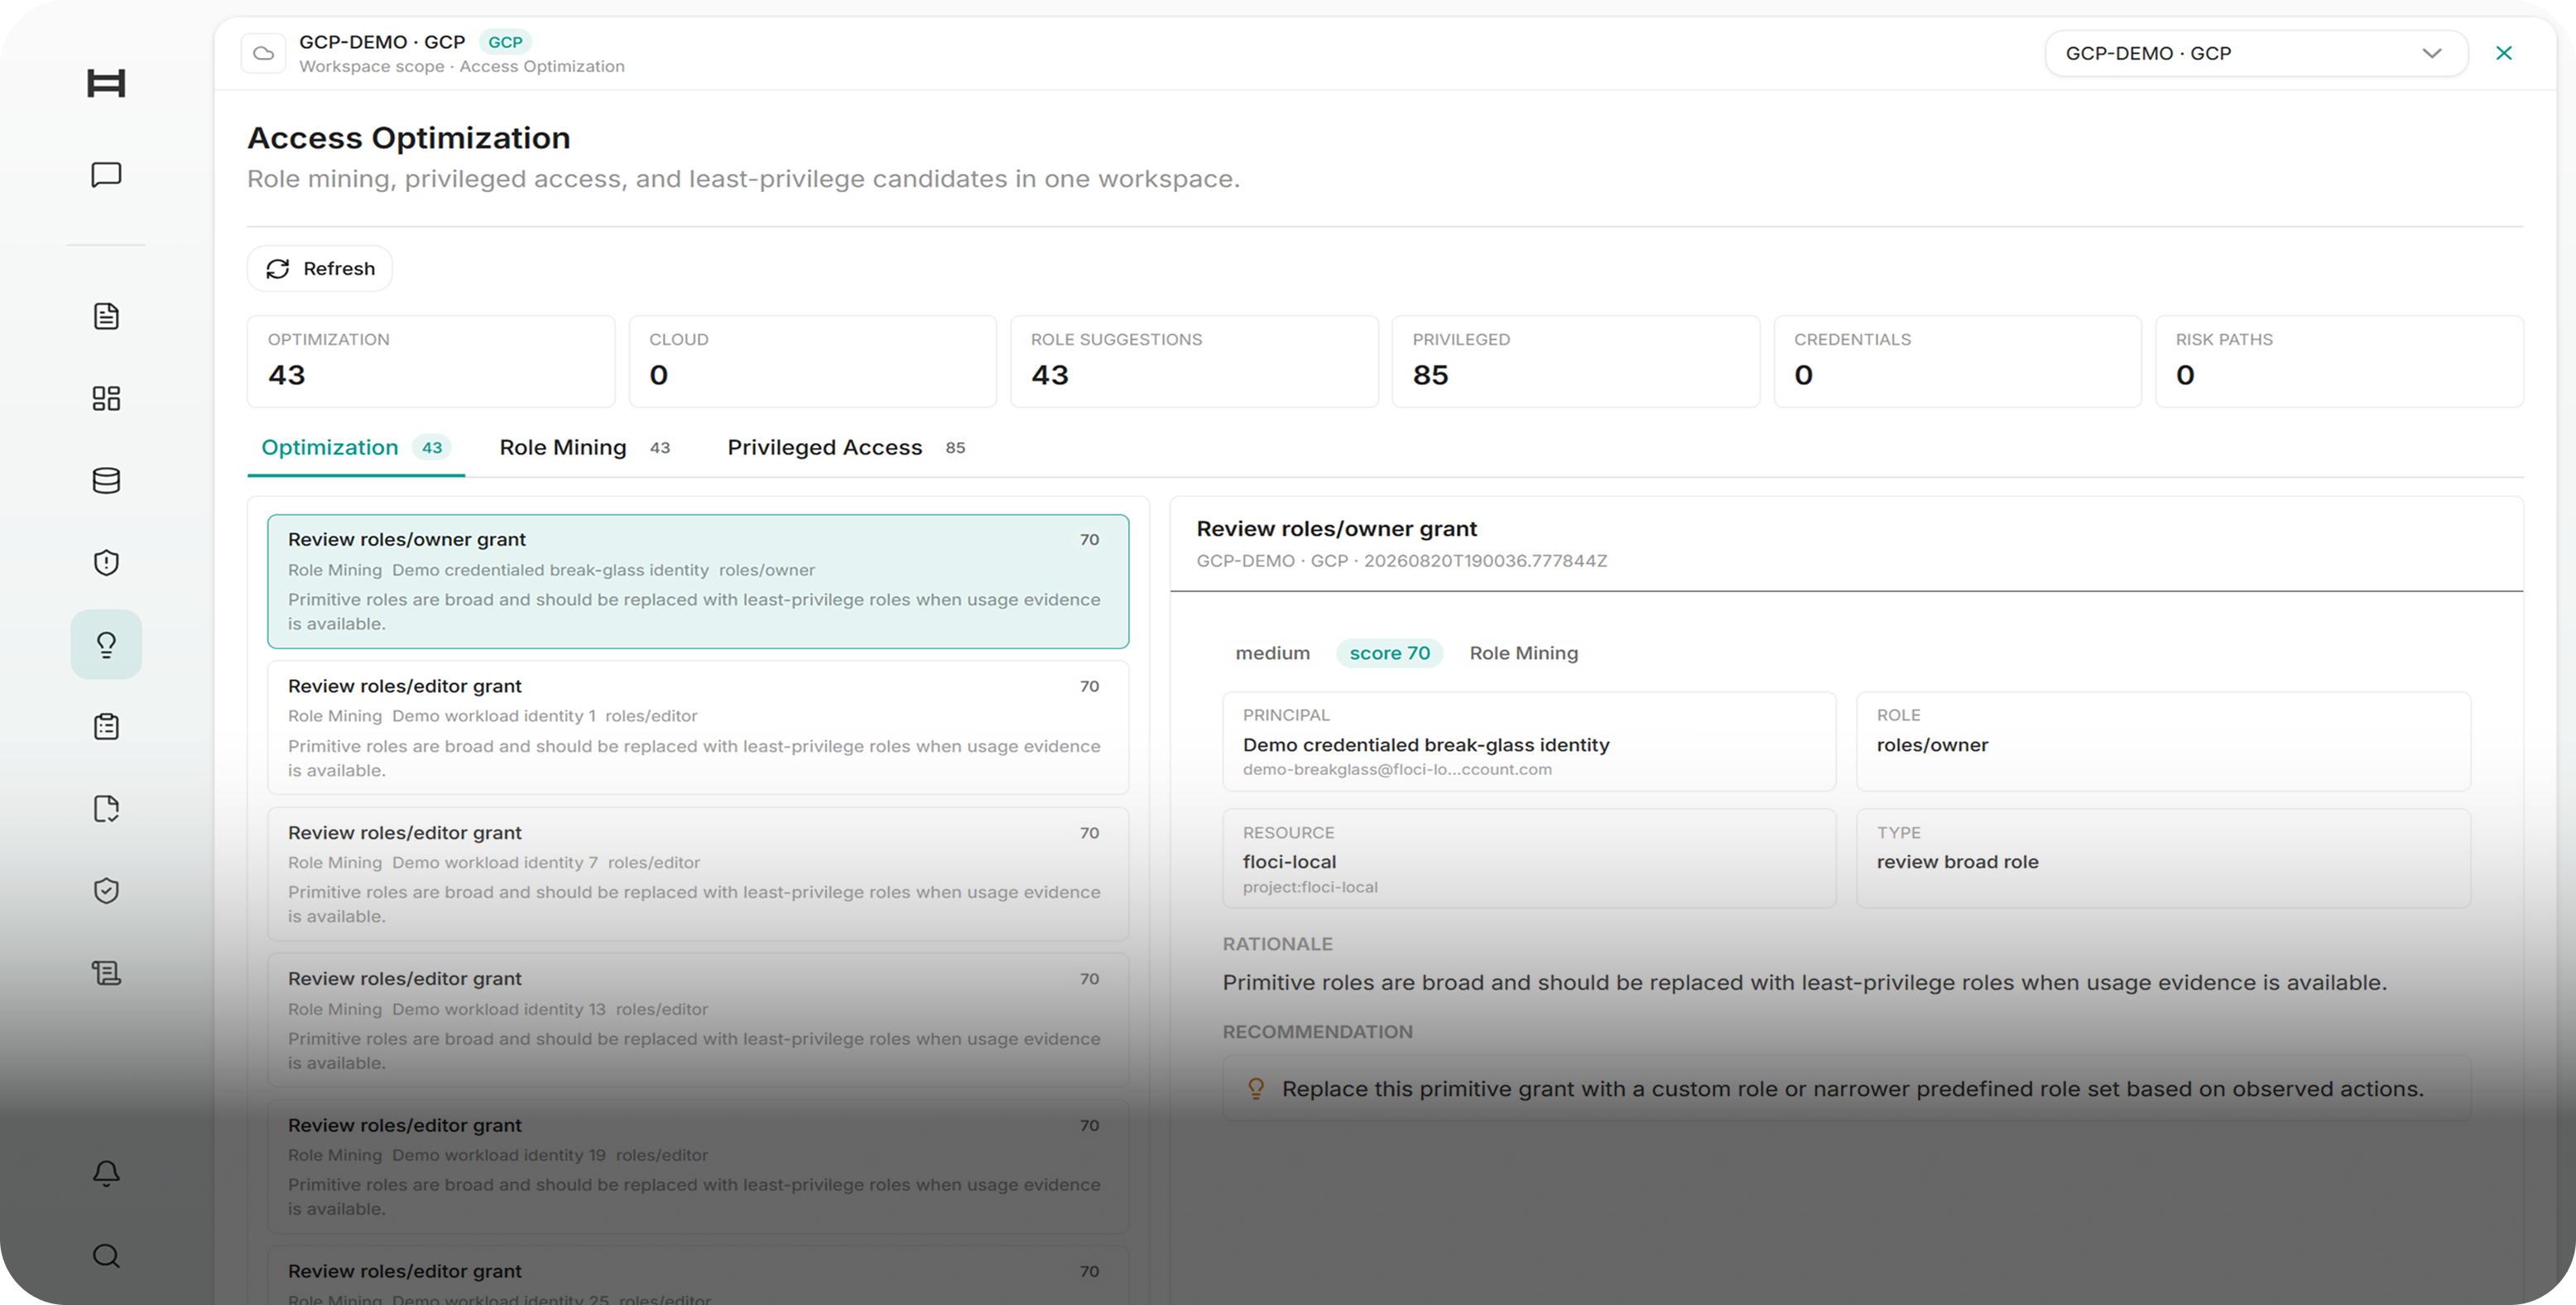
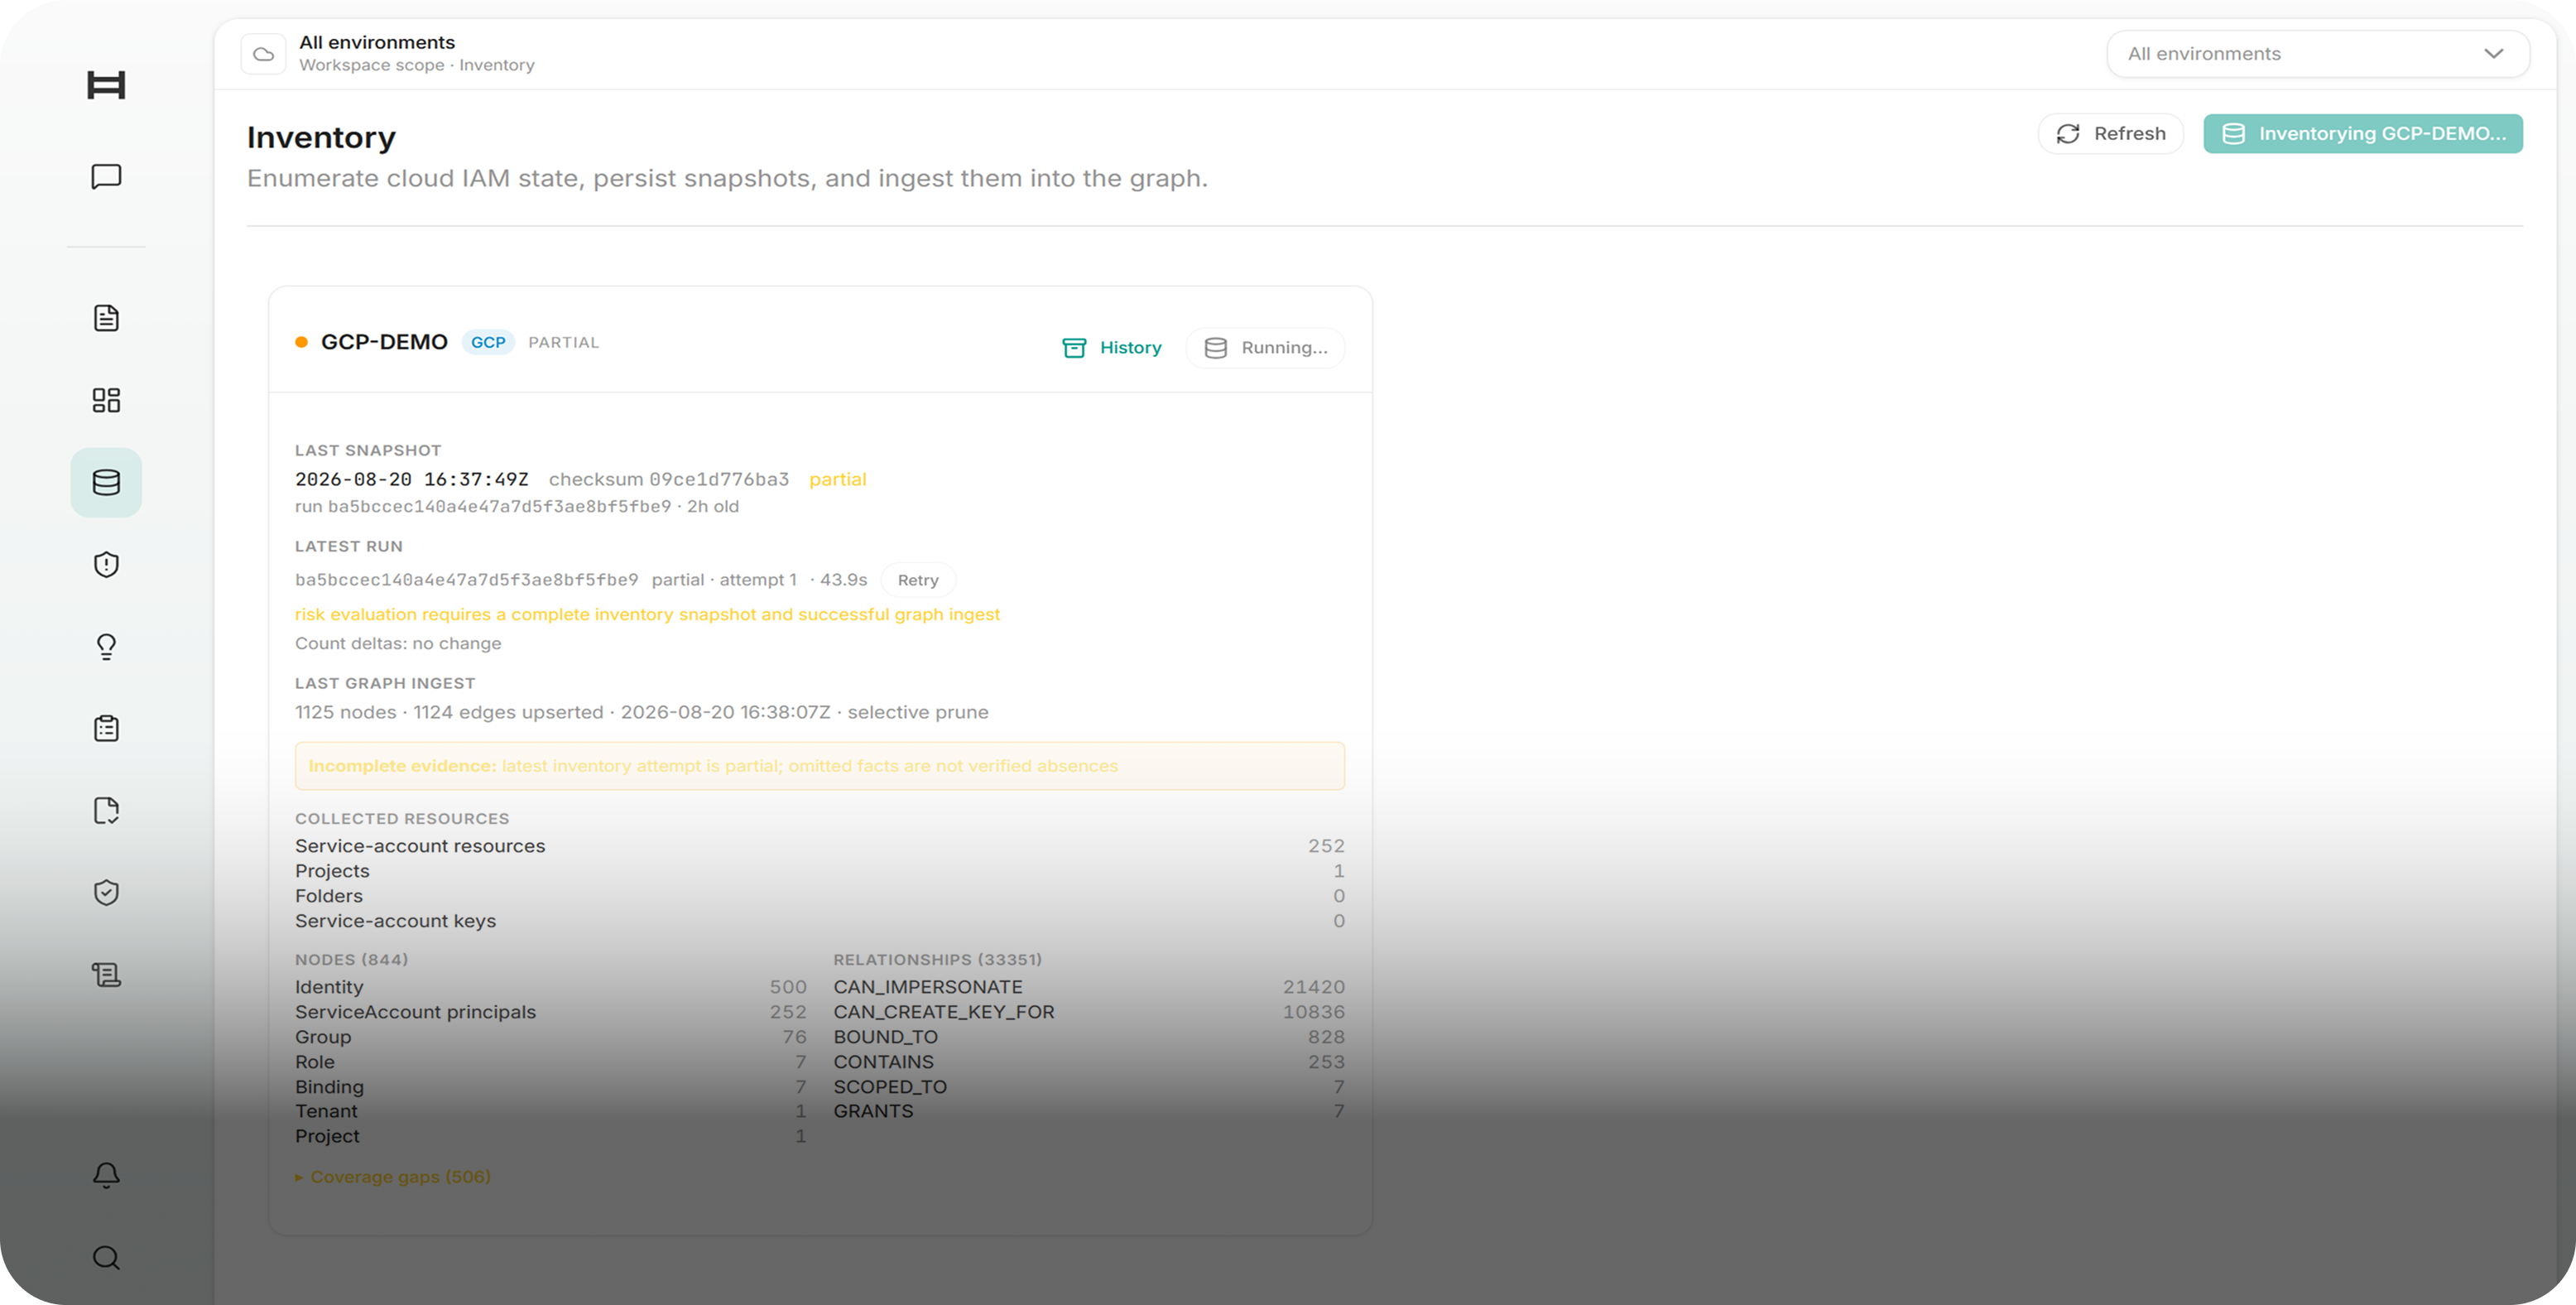
Cross-Cloud Identity and Entitlement Graph with Normalization
IAM
HUB
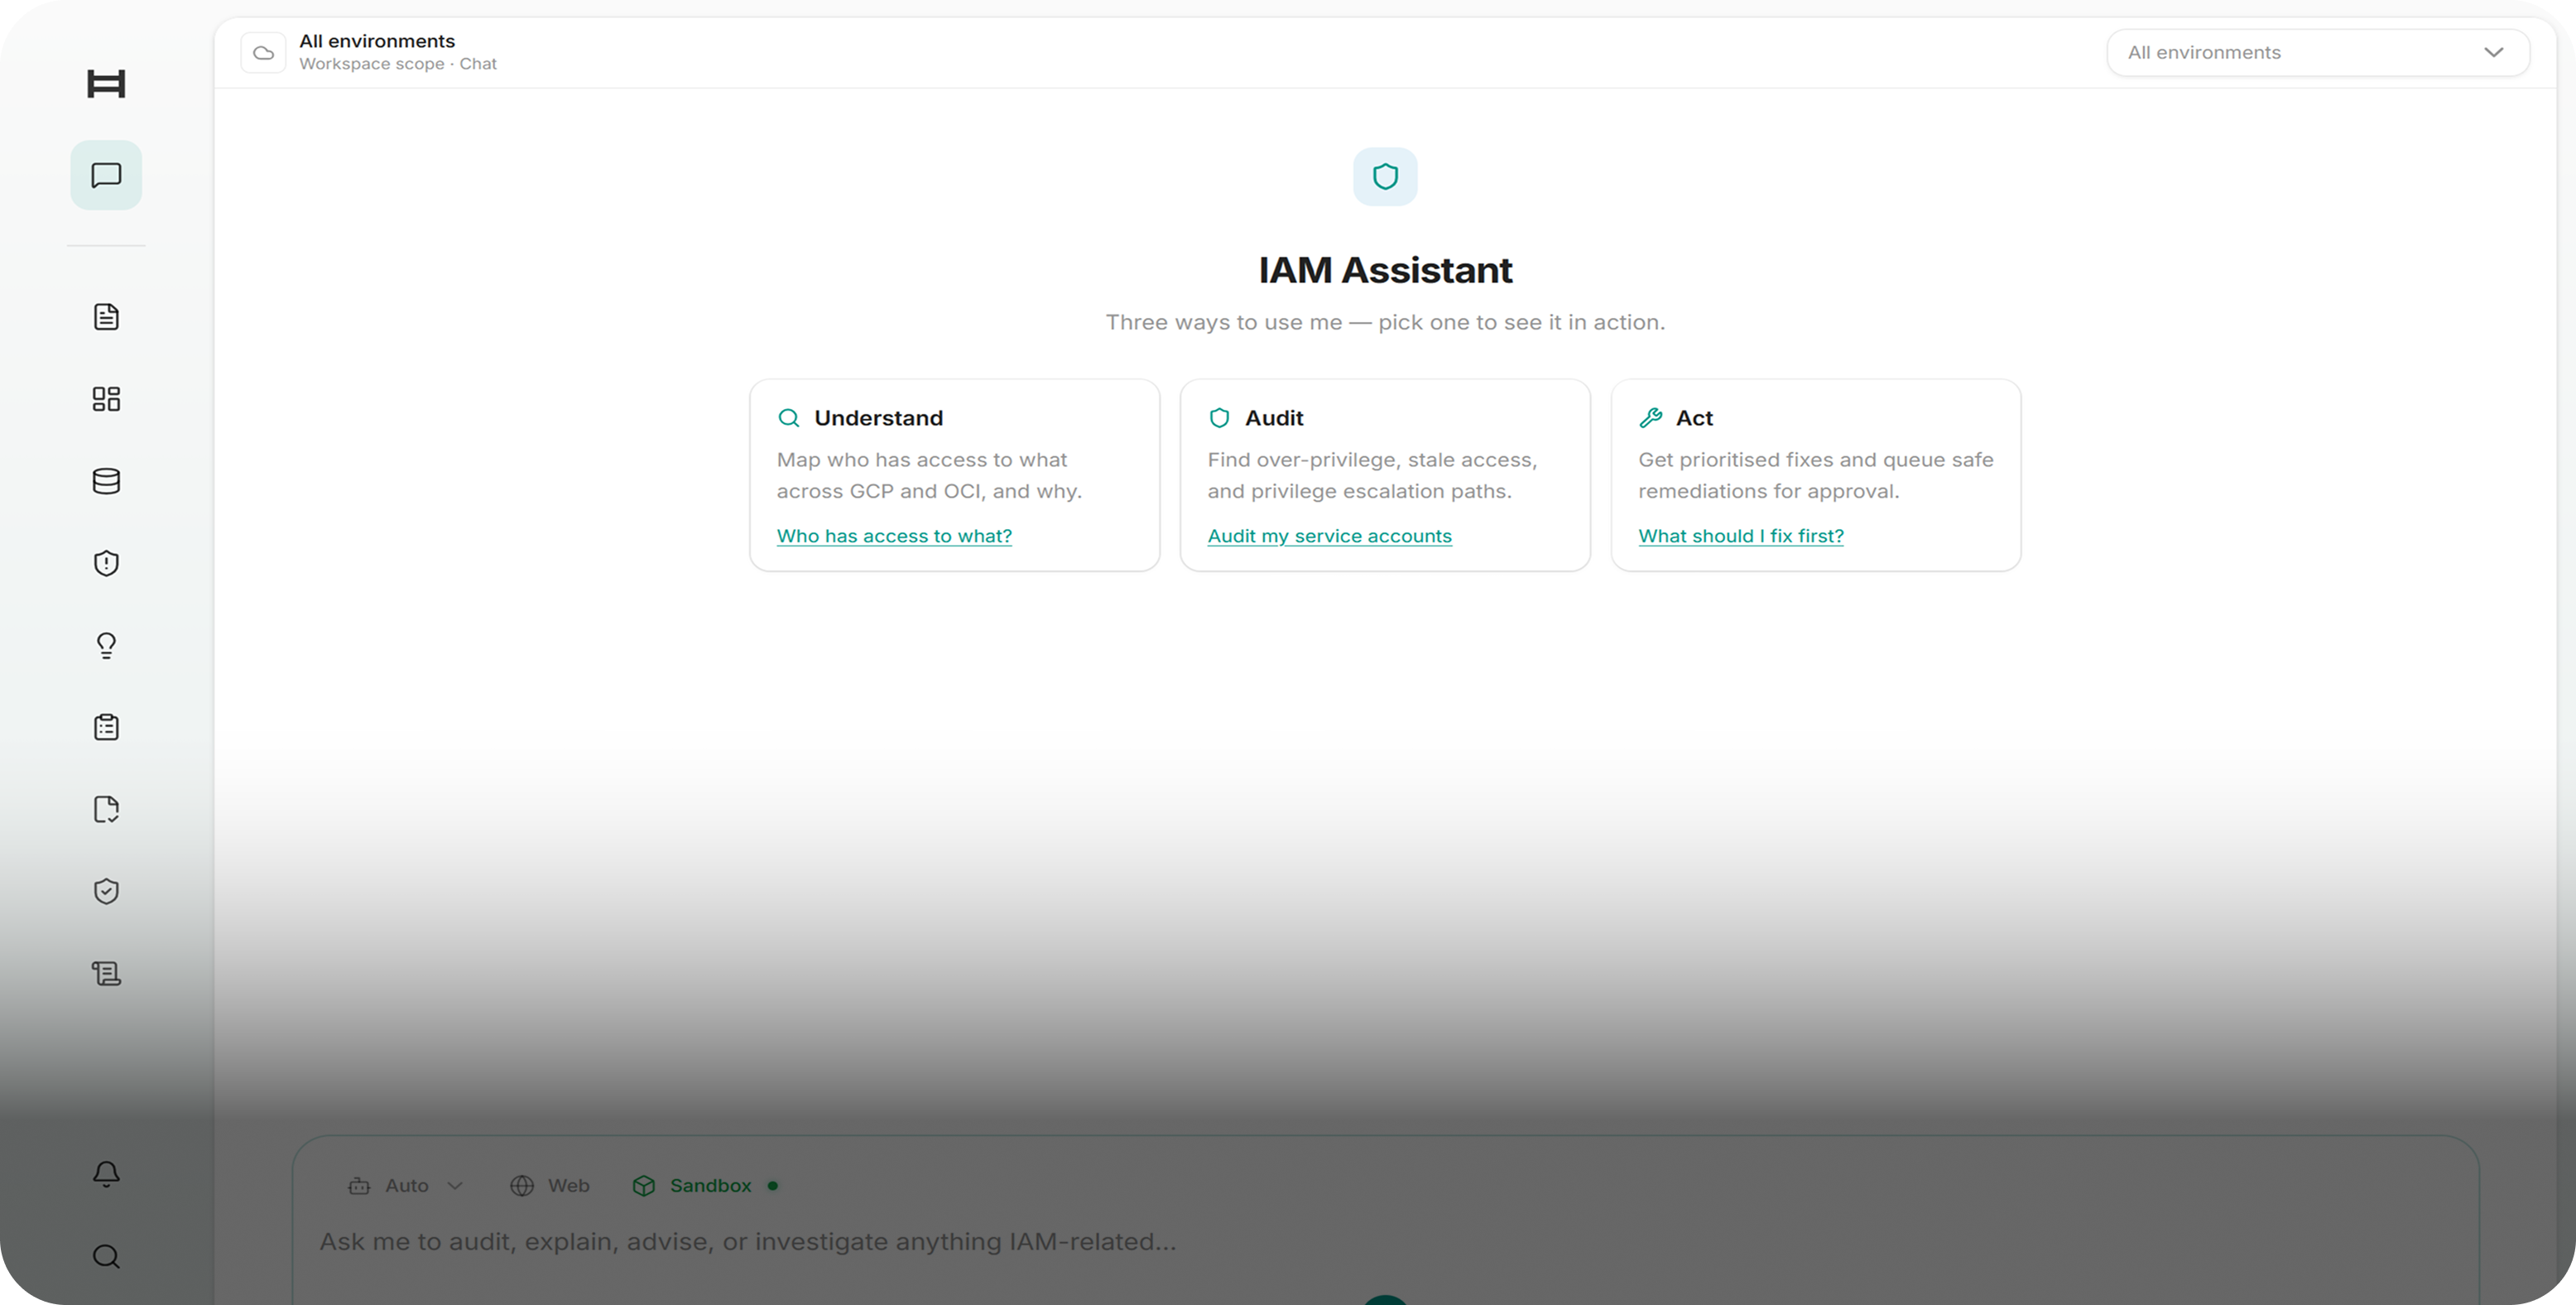
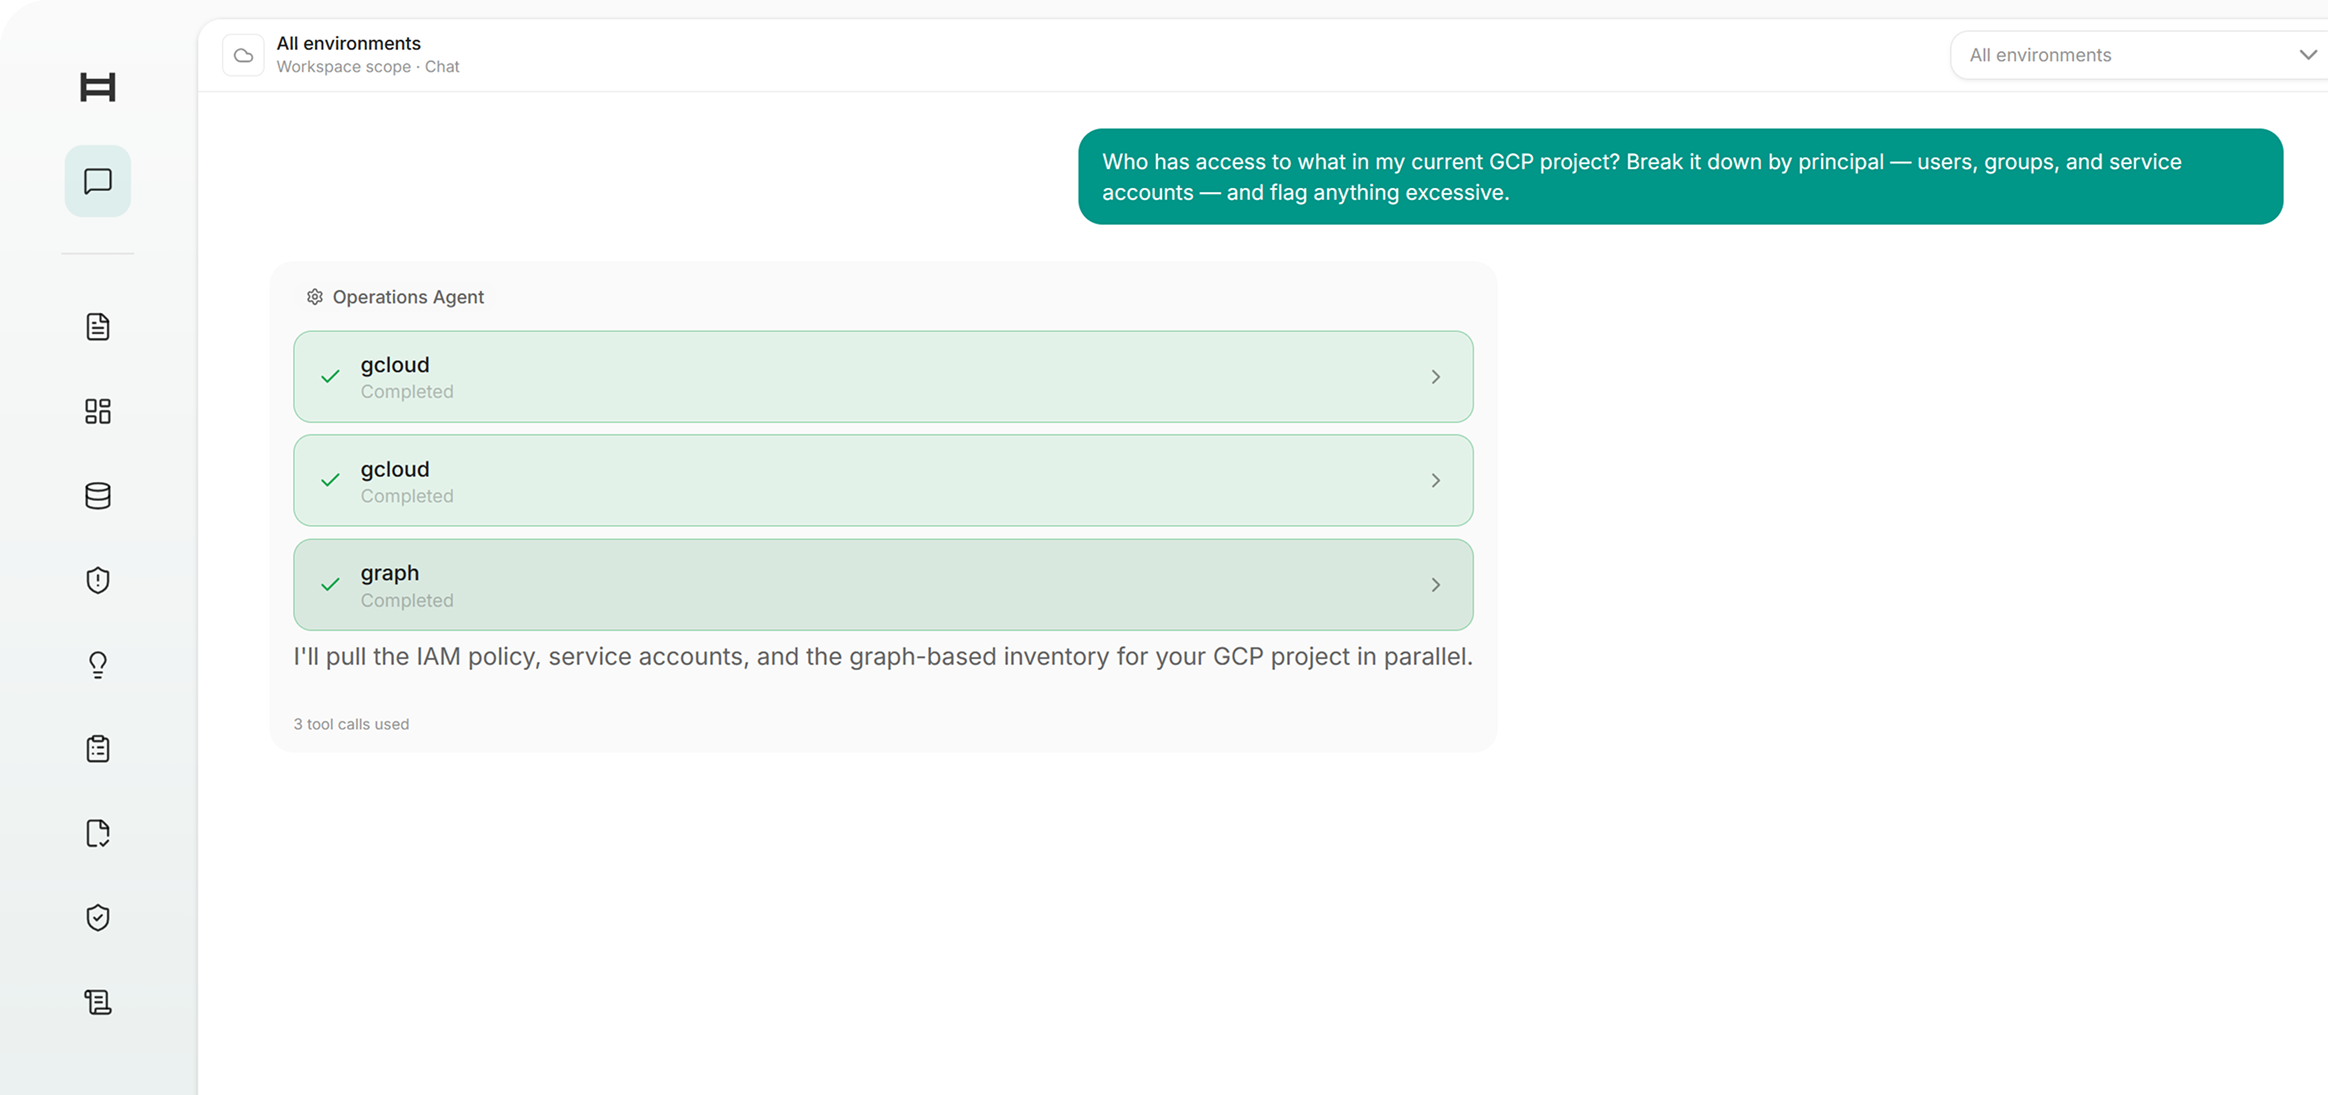
Conversational Plain-English IAM Audit Copilot for GCP and OCI
SOC
& SIEM
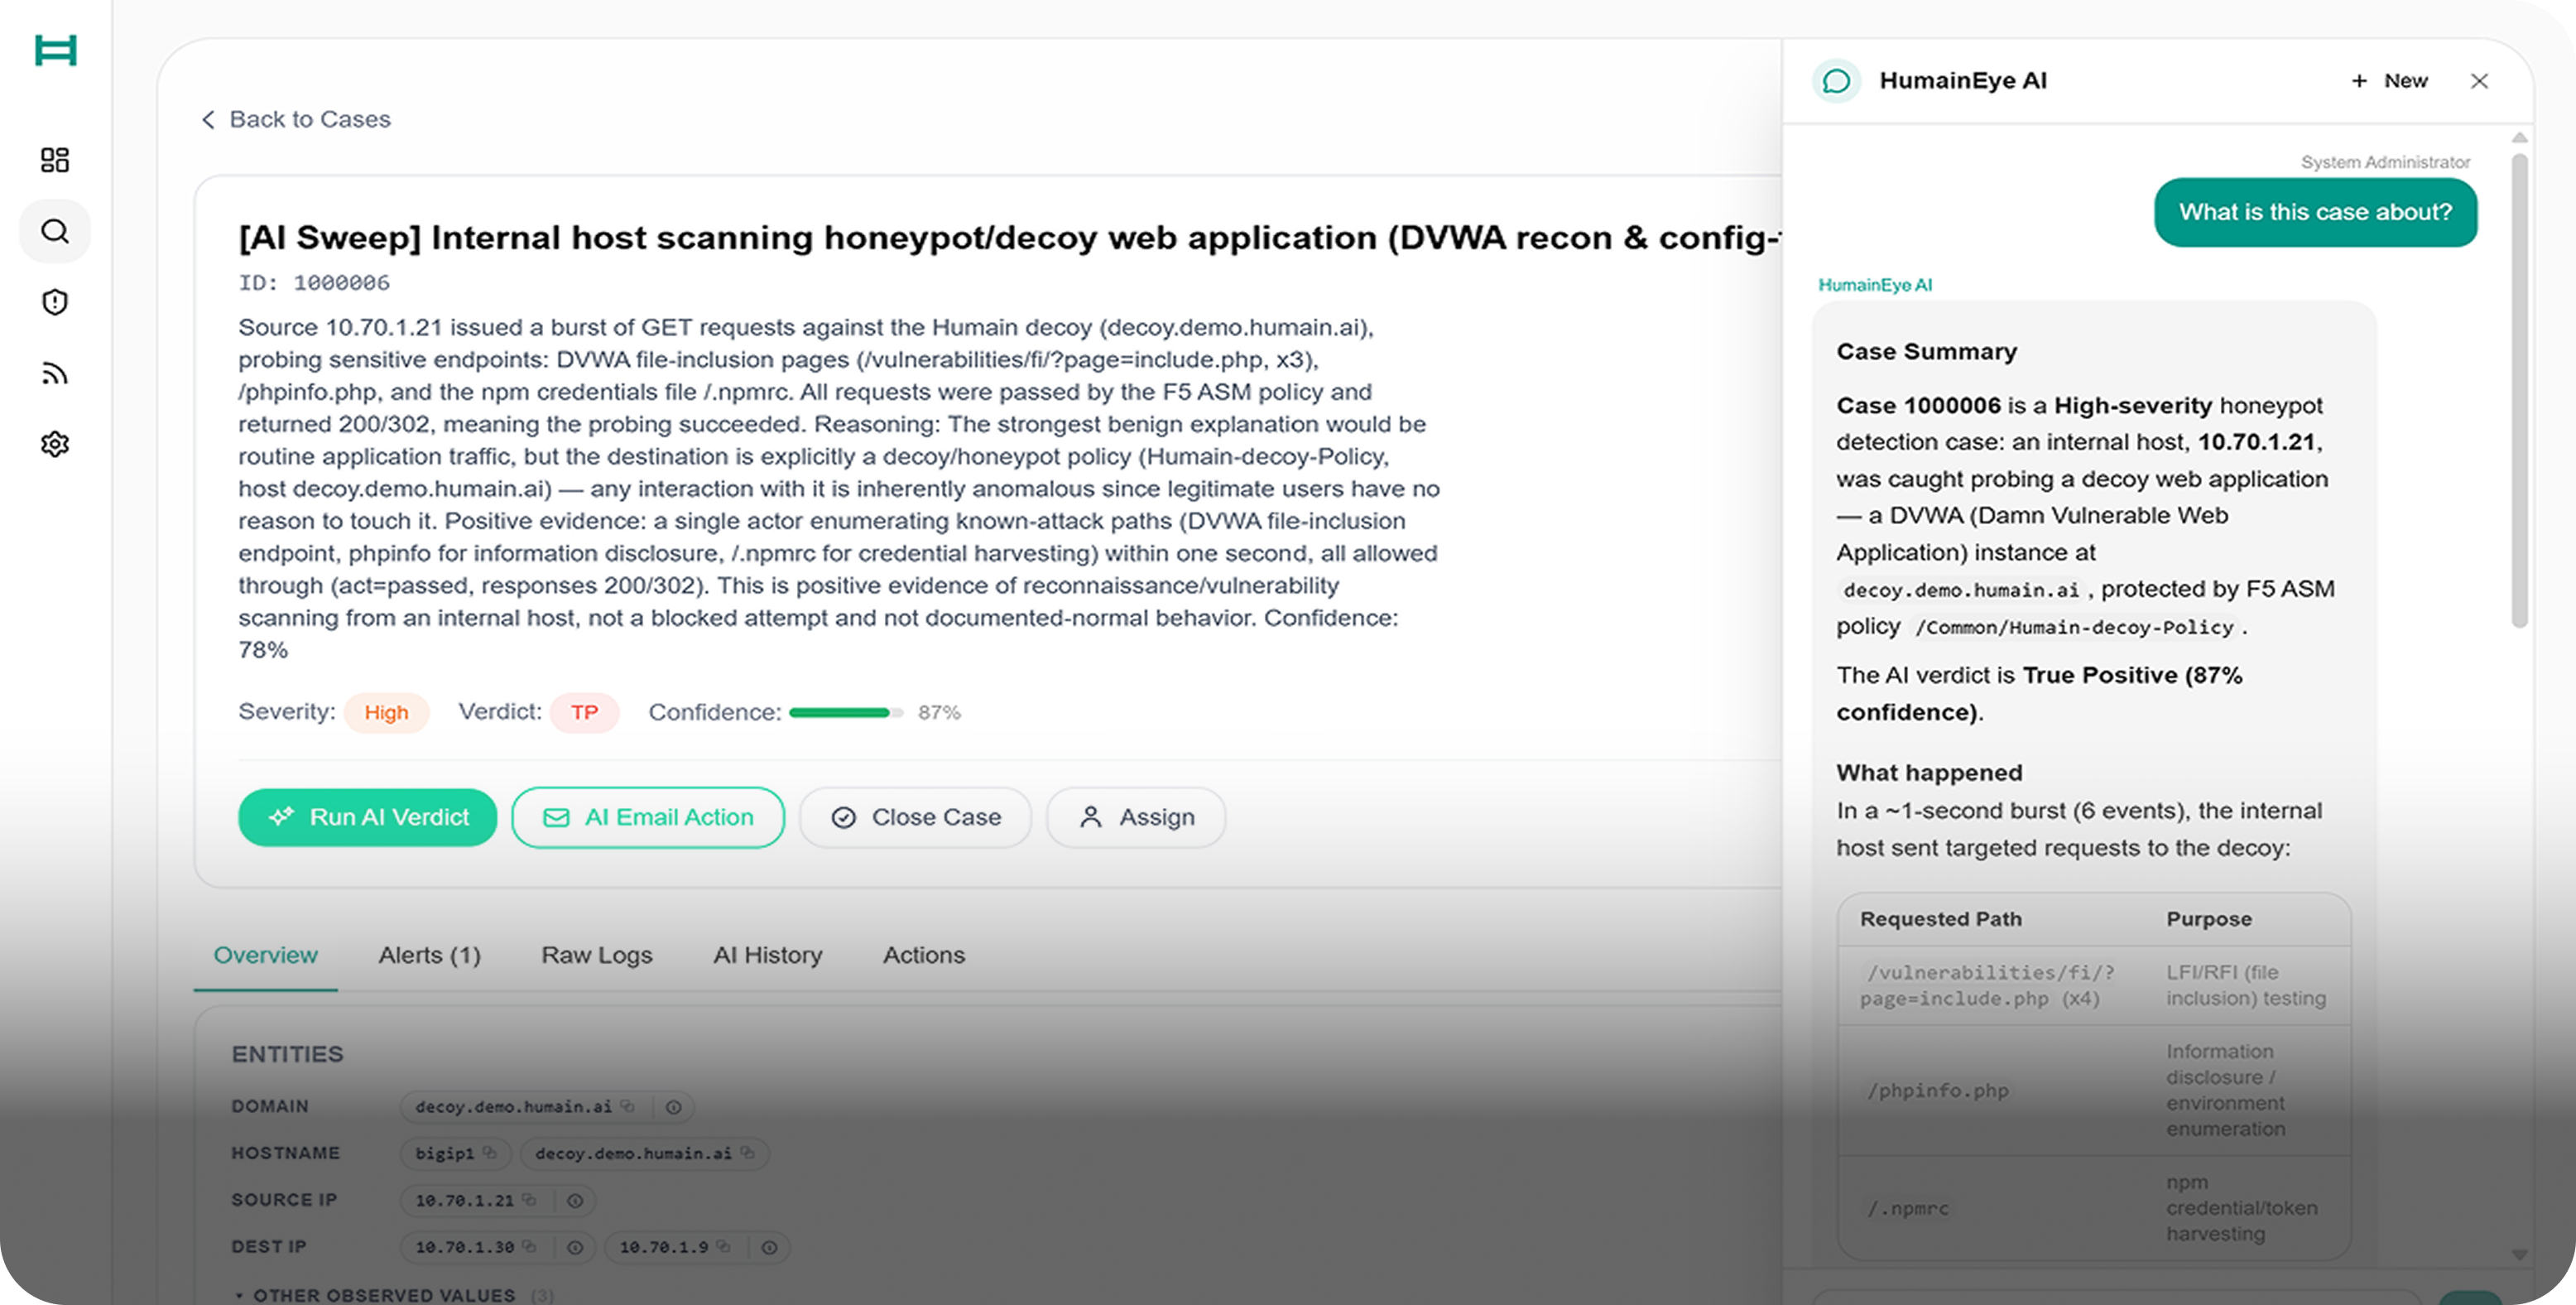
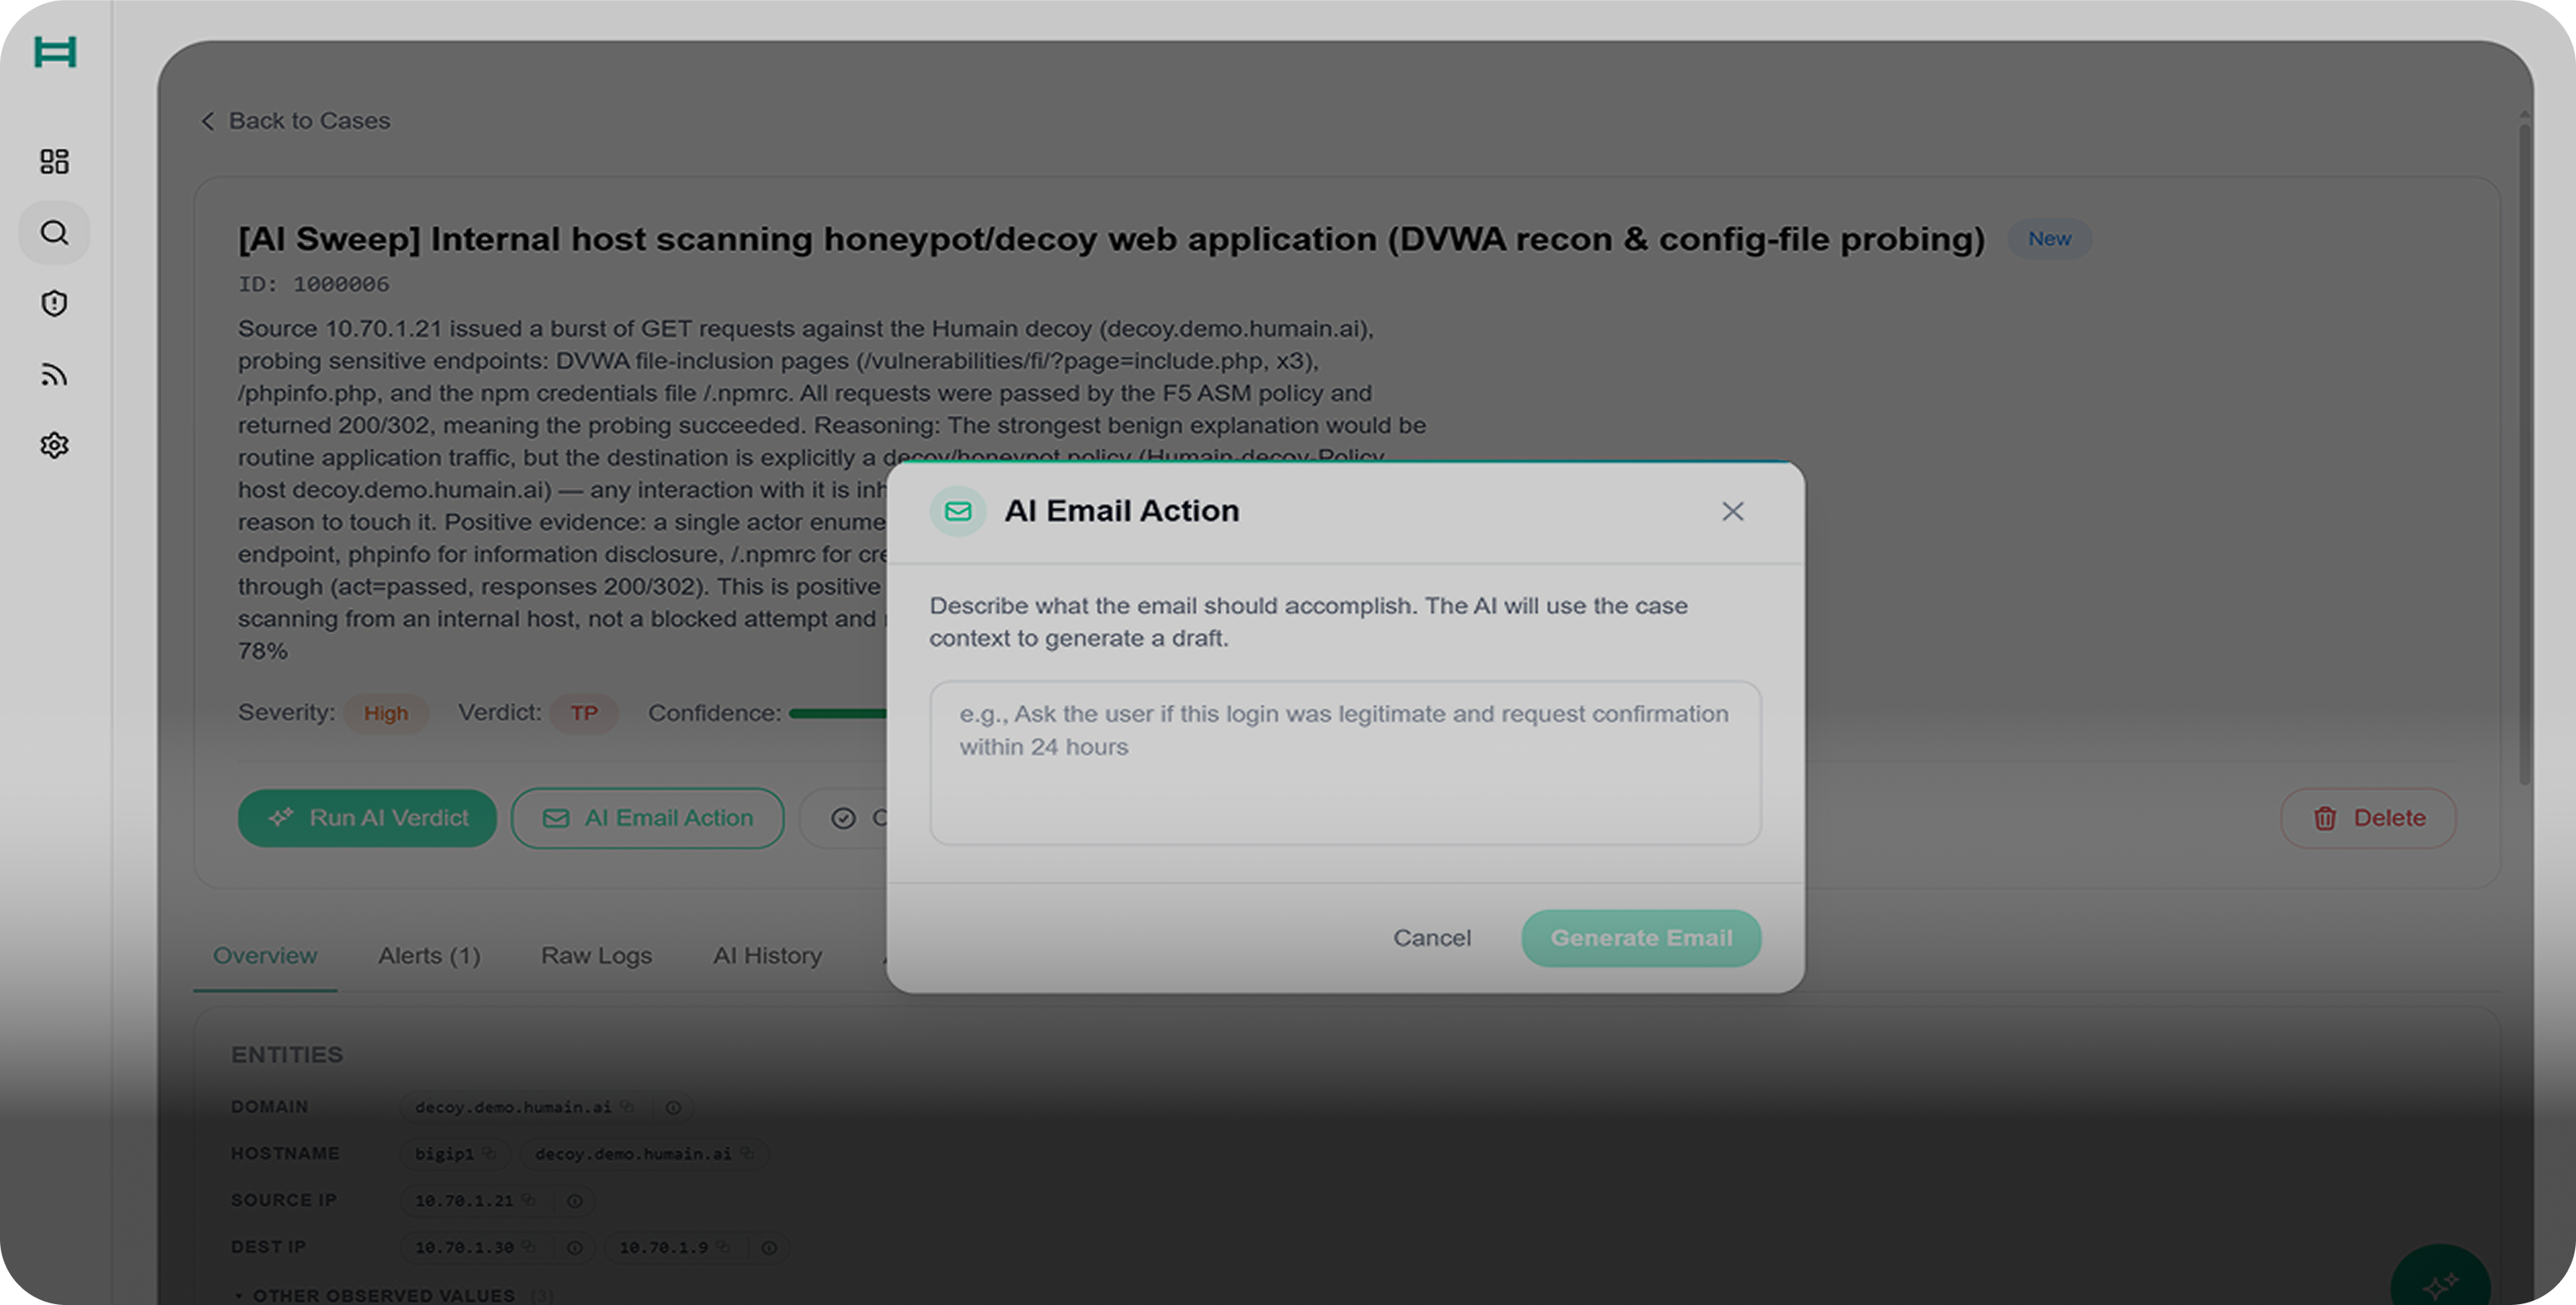
Automated Investigation Emails with Reply Monitoring and Responding
SOC
& SIEM
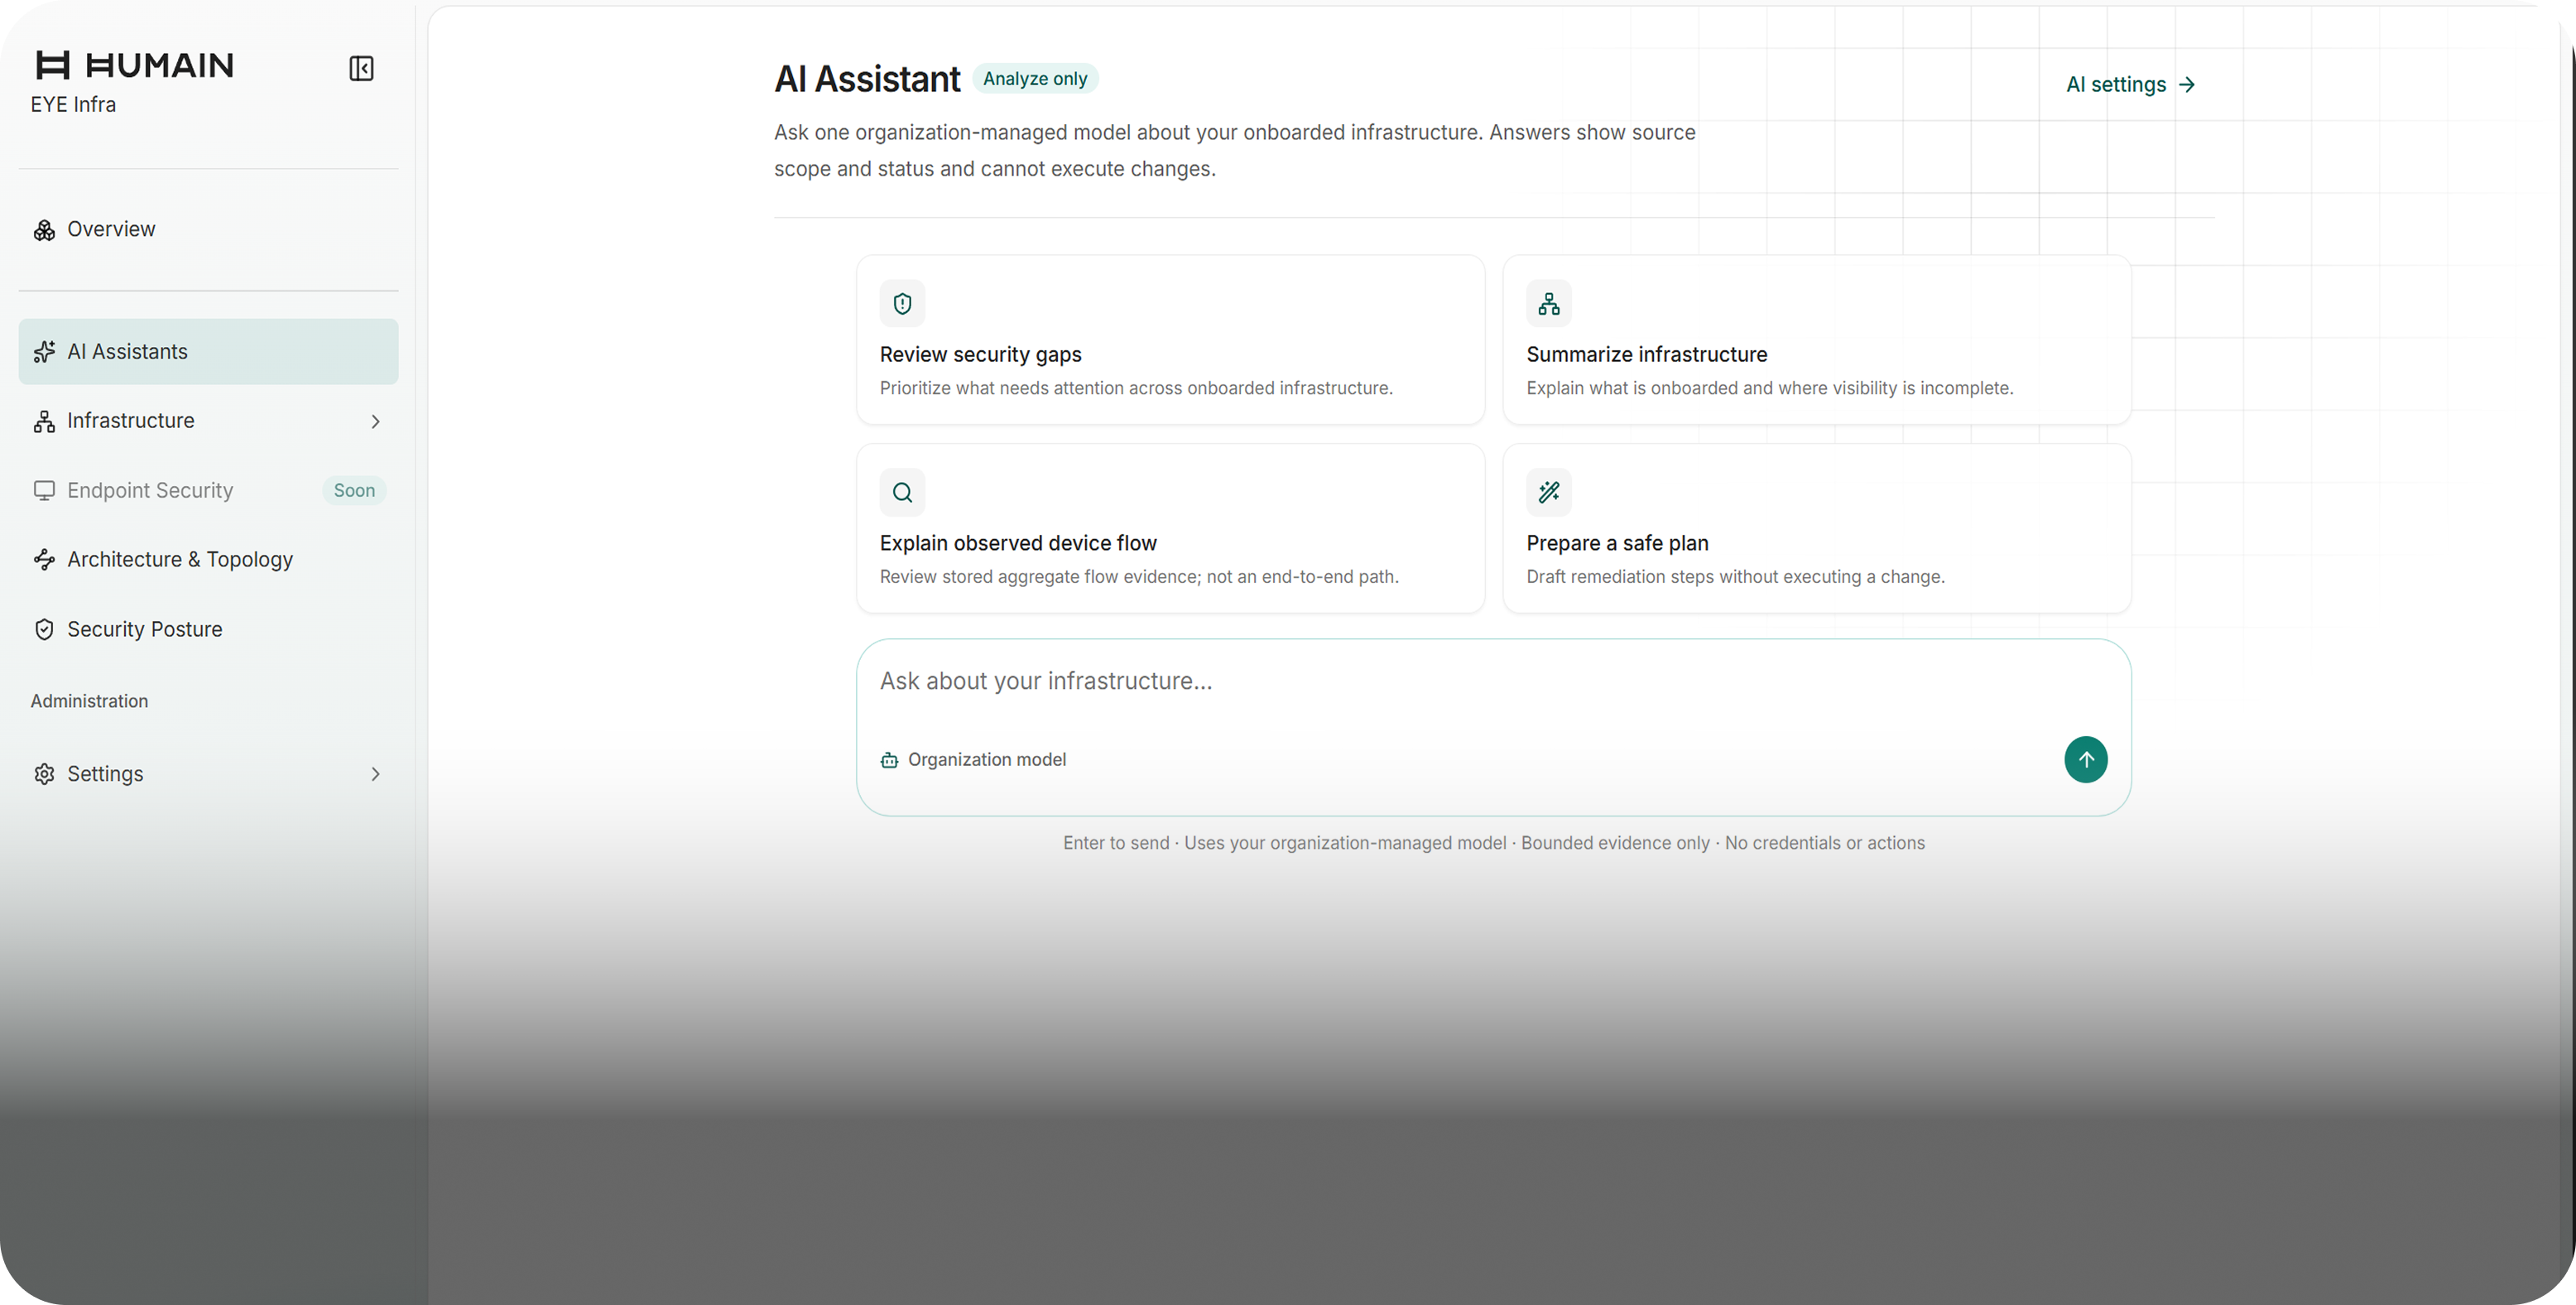
AI Analyst Chat Grounded in Full Case Context
IAM
HUB
Full Command Transparency and Agent Action Audit Trail
IAM
HUB
Scoped Read-Only Cloud Connectors with Credential Vaulting (GCP + OCI)
INFRA
SECURITY
Agentless Cloud Misconfiguration Scanning (CSPM) with CIS and NCA ECC/SAMA Policy Packs
CLOUD
SECURITY
Continuous Compliance Monitoring for Cloud Environments with Custom Policy Templates
INFRA
SECURITY
Unified Posture & Coverage Dashboard
APPLICATION SECURITY
Rules-of-Engagement Control Plane, In-Path Scope Enforcement and Ten-Second Kill Switch
APPLICATION SECURITY
Authorized Campaign and Target Configuration
SOC
& SIEM
Deterministic Rules Engine for Sub-Second Auto-Close
SOC
& SIEM
Confidence-Thresholded LLM Auto-Close with Human Override
SOC
& SIEM
LLM Verdict Pipeline for Tier-1 Alert Triage
SOC
& SIEM
Case Timeline, Evidence Pack and Executive Summary
SOC
& SIEM
Raw Log Ingestion Platform (Any source)
IAM
HUB
One-Click PDF Audit Evidence Reports Mapped to NCA ECC, SAMA CSF and ISO 27001
IAM
HUB
Environment Baseline and Approved-Exception Memory
INFRA
SECURITY
Asset Lifecycle Governance: Classification, Ownership and Approval Gates
INFRA
SECURITY
Cloud & Kubernetes Read-Only Onboarding Connectors with Least-Privilege Templates
APPLICATION SECURITY
Cross-Scanner Deduplication & Canonical Vulnerability Identity Resolution
APPLICATION SECURITY
Latest-Commit Changed-Code Review
APPLICATION SECURITY
Secure Self-Hosted GitLab Repository Onboarding
INFRA
SECURITY
Unified Asset & Application Inventory with Cross-Source Deduplication
INFRA
SECURITY
Symantec Endpoint Integration with Endpoint & Patch Hygiene Scoring
APPLICATION SECURITY
Multi-Scanner Findings Ingestion & Normalisation Pipeline (Qualys, Tenable, Sysdig, Nessus,
CSV/SARIF)
IAM
HUB
Cross-Cloud Identity and Entitlement Graph with Normalization
IAM
HUB
Conversational Plain-English IAM Audit Copilot for GCP and OCI
SOC
& SIEM
Automated Investigation Emails with Reply Monitoring and Responding
SOC
& SIEM
AI Analyst Chat Grounded in Full Case Context
IAM
HUB
Full Command Transparency and Agent Action Audit Trail
IAM
HUB
Scoped Read-Only Cloud Connectors with Credential Vaulting (GCP + OCI)


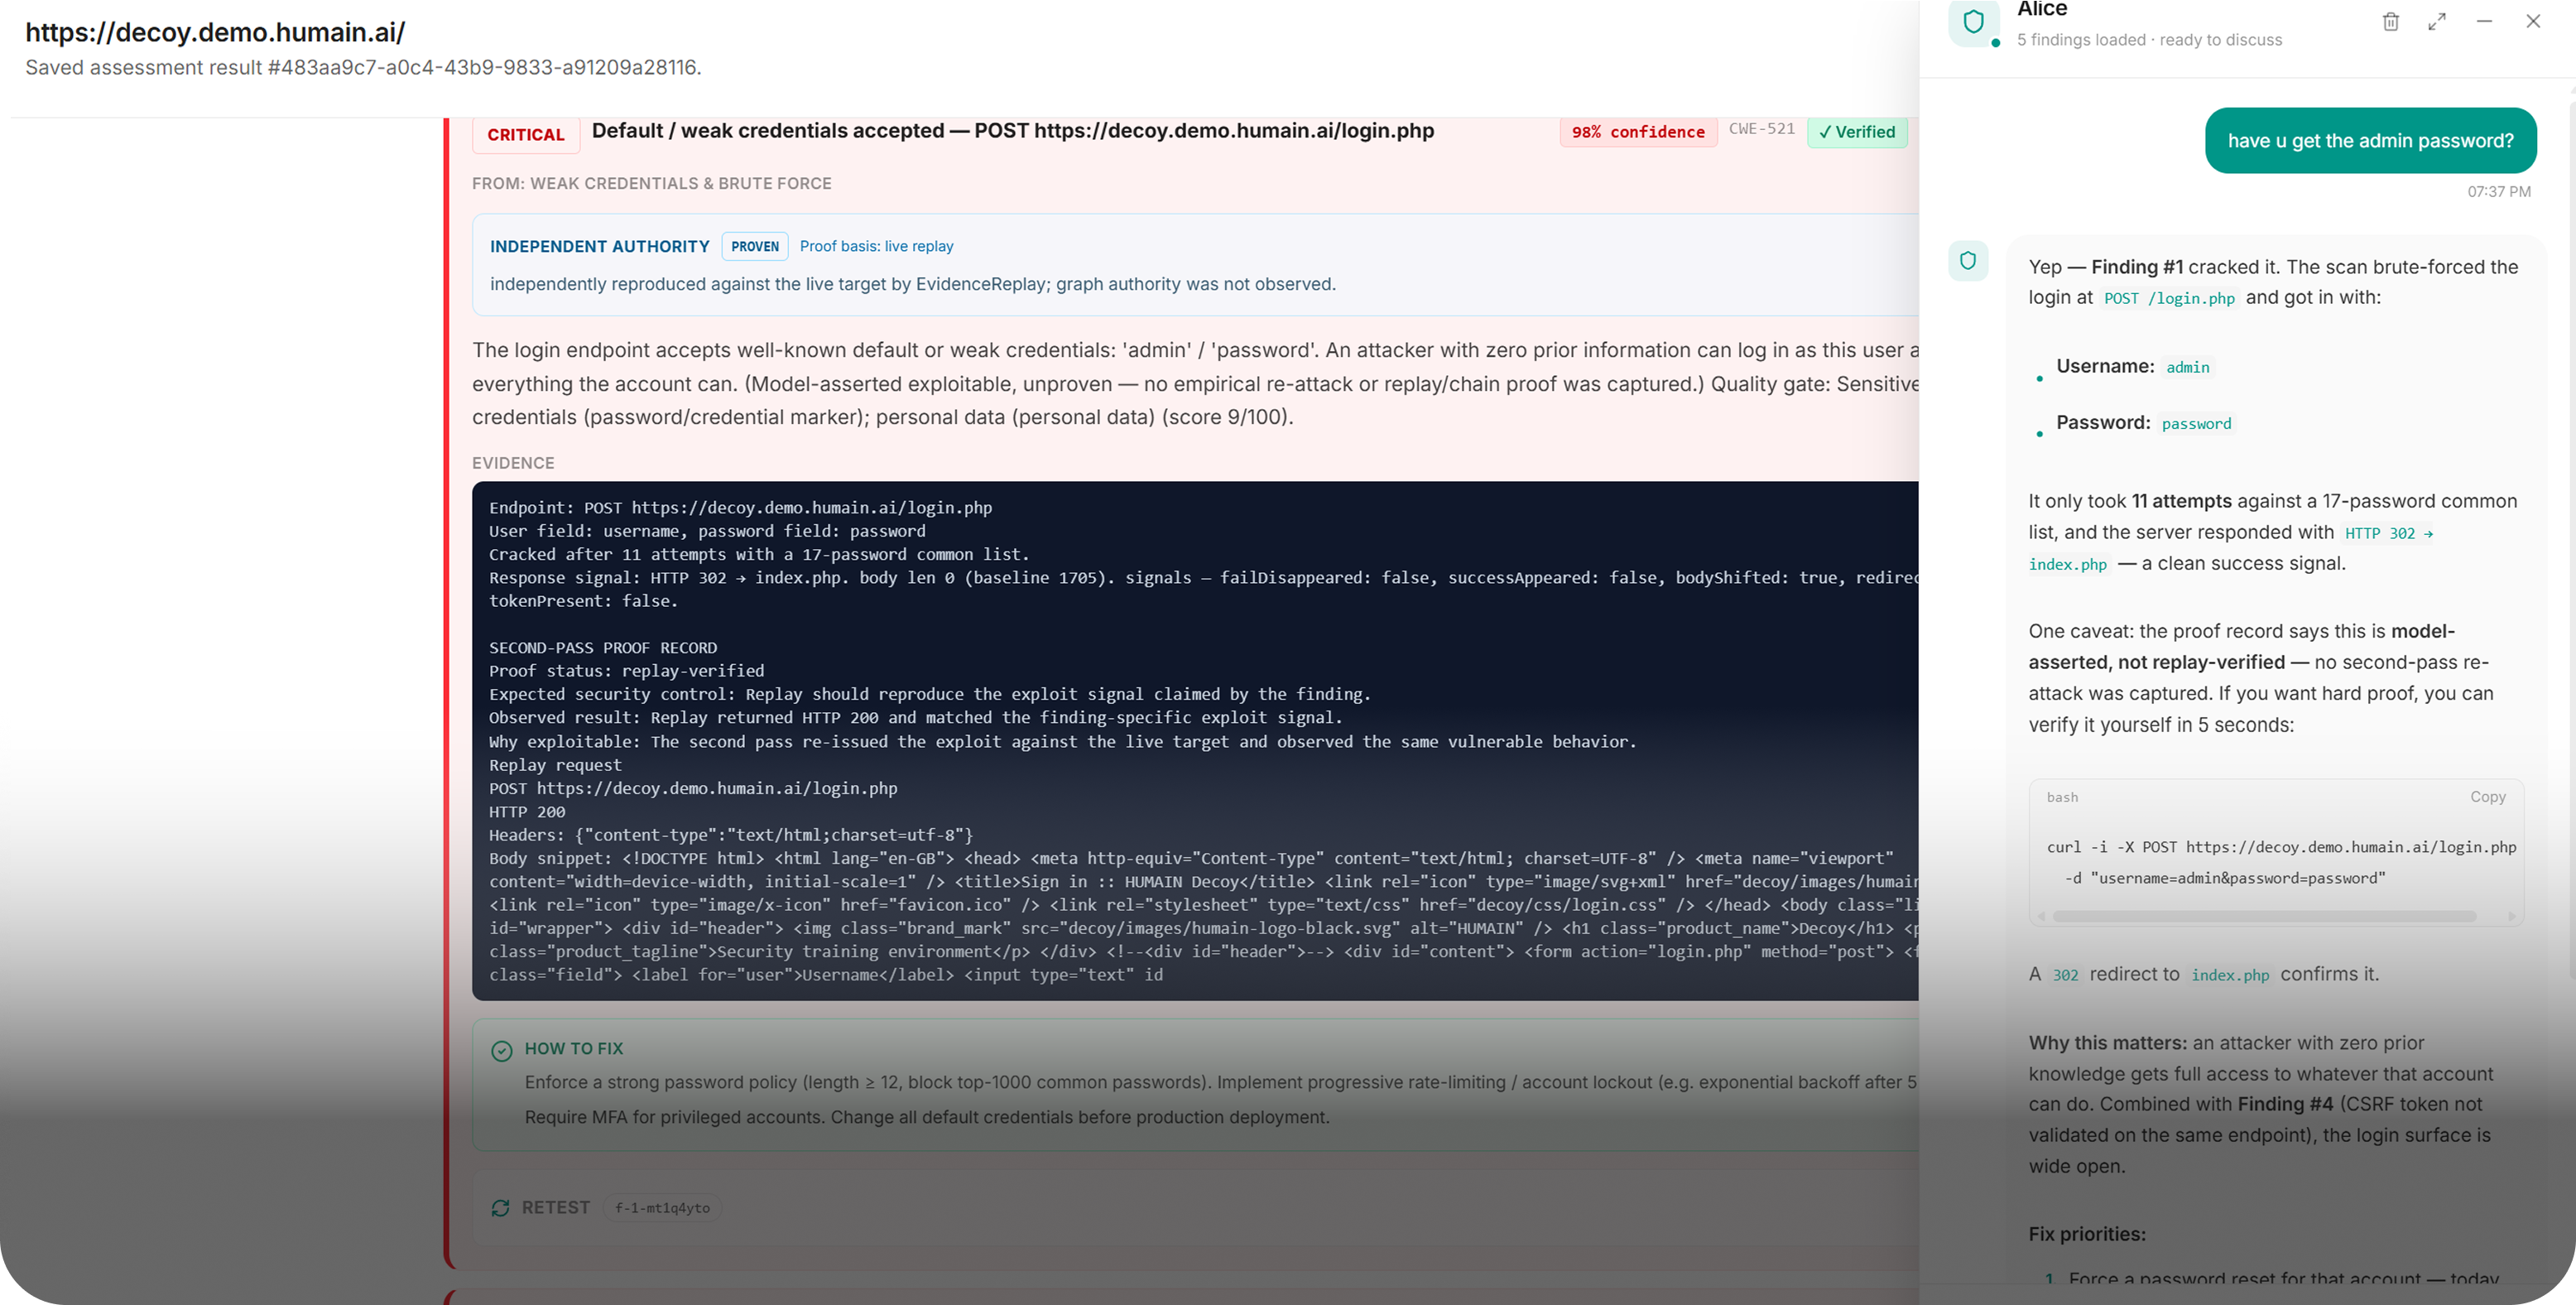
 Real, proven risk